
Cybersecurity Tech Brief By HackerNoon
HackerNoon
0
Cybersecurity Tech Brief By HackerNoon provides concise updates on the latest developments in cybersecurity. Each episode covers recent news, threats, and trends in the tech world, aimed at keeping listeners informed about digital security. The podcast is produced by HackerNoon, a technology media platform.
Jaksot
-
 Securing Inherited AI: Models, Runtimes, and Tools Inside Vendor Software 17.09.2026 12minThis story was originally published on HackerNoon at: https://hackernoon.com/securing-inherited-ai-models-runtimes-and-tools-inside-vendor-software. AI models can enter your infrastructure through vendor software. Learn how to inventory inherited AI, assess its permissions, and manage supply chain risk. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #ai-security, #enterprise-ai, #inherited-ai-risk, #ai-supply-chain-security, #embedded-ai, #ai-bill-of-materials, #model-provenance, #third-party-ai-risk, and more. This story was written by: @rpinto. Learn more about this writer by checking @rpinto's about page, and for more stories, please visit hackernoon.com. Vendor software can introduce models, runtimes, retrieval pipelines, and agent tools into an organization’s infrastructure. Security teams should inventory these components, verify provenance, restrict access, and monitor behavior rather than assume existing vendor reviews cover them.
-
 AI Slop Is Creating a New Kind of Technical Debt 17.09.2026 7minThis story was originally published on HackerNoon at: https://hackernoon.com/ai-slop-is-creating-a-new-kind-of-technical-debt. AI-generated code can work perfectly and still become a liability. Here’s why comprehension debt may be the real danger of AI coding. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #api, #artificial-intelligence, #career, #content-creation, #git, #ai-generated-code, #comprehension-debt, and more. This story was written by: @soladipupo. Learn more about this writer by checking @soladipupo's about page, and for more stories, please visit hackernoon.com. AI-generated code can work perfectly and still become a liability. Here’s why comprehension debt may be the real danger of AI coding.
-
 What the NetNut Takedown Reveals About Residential Proxy Sourcing 16.09.2026 4minThis story was originally published on HackerNoon at: https://hackernoon.com/what-the-netnut-takedown-reveals-about-residential-proxy-sourcing. NetNut's takedown exposed a structural sourcing problem in residential proxies, and why owned infrastructure is what actually matters. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #web-scraping, #data-privacy, #botnets, #proxy-servers, #netnu, #proxy-sourcing, #netnu-takedown, and more. This story was written by: @marae. Learn more about this writer by checking @marae's about page, and for more stories, please visit hackernoon.com. NetNut's residential proxy network was disrupted by the FBI and Google in July 2026, after reporting found a large share of its IP pool was sourced from compromised devices. The deeper issue is structural, most residential proxy brands resell capacity from upstream networks they don't directly control, which makes sourcing nearly impossible for buyers to verify. A small number of providers, including Bright Data and Squid Proxies, own their infrastructure outright instead of reselling, which is the actual difference worth checking before trusting any "ethically sourced" claim.
-
 SecurityMetrics Contributes to GEAR, Shares AI Solutions at the PCI SSC NA 2026 Community Meeting 15.09.2026 3minThis story was originally published on HackerNoon at: https://hackernoon.com/securitymetrics-contributes-to-gear-shares-ai-solutions-at-the-pci-ssc-na-2026-community-meeting. SecurityMetrics contributes to GEAR and shares AI solutions at PCI SSC NA Community Meeting. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #future-of-ai, #compliance, #pci-compliance, #pci-dss, #merchantsolutions, #ecommerce, #good-company, and more. This story was written by: @pr-securitymetrics. Learn more about this writer by checking @pr-securitymetrics's about page, and for more stories, please visit hackernoon.com. SecurityMetrics is contributing to GEAR and announcing AI solutions at this year's PCI SSC NA Community Meeting.
-
 How Fraud Rings Hide in Plain Sight: A Confidence-Weighted Framework for Linkage Analysis 14.09.2026 16minThis story was originally published on HackerNoon at: https://hackernoon.com/how-fraud-rings-hide-in-plain-sight-a-confidence-weighted-framework-for-linkage-analysis. A vendor-neutral framework for weighing links in fraud graphs, limiting risk propagation, and separating associations from reviewed decisions. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #fraud-detection, #speech-recognition, #graph-based-fraud-detection, #fraud-linkage-analysis, #heterophilic-graphs, #risk-propagation, #graph-neural-networks, #fraud-model-evaluation, and more. This story was written by: @nissan-modi. Learn more about this writer by checking @nissan-modi's about page, and for more stories, please visit hackernoon.com. The article proposes R-U-T-C, a conceptual framework for evaluating the reliability, uniqueness, timing, and corroboration of links in fraud graphs without treating association as automatic guilt.
-
 7 Questions for Assessing Cyber Resilience Act Codebase Readiness 12.09.2026 14minThis story was originally published on HackerNoon at: https://hackernoon.com/7-questions-for-assessing-cyber-resilience-act-codebase-readiness. Assess your codebase for Cyber Resilience Act readiness with seven practical security questions ahead of the EU's 2026 reporting requirements. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #finance, #programming, #software-development, #artificial-intelligence, #authentication, #cra-compliance, #cra-reporting, and more. This story was written by: @sonarsource. Learn more about this writer by checking @sonarsource's about page, and for more stories, please visit hackernoon.com. Assess your codebase for Cyber Resilience Act readiness with seven practical security questions ahead of the EU's 2026 reporting requirements.
-
 What Happens to Your Data After You Hit Allow 11.09.2026 4minThis story was originally published on HackerNoon at: https://hackernoon.com/what-happens-to-your-data-after-you-hit-allow. Tapping allow is just the start. Learn what really happens to your data afterward, from storage and reuse to third party sharing and deletion rules. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #internet-privacy, #data-privacy, #data-retention, #privacy-policies, #ftc-data-brokers, #data-collection, #app-privacy, #consumer-privacy, and more. This story was written by: @techprivacy. Learn more about this writer by checking @techprivacy's about page, and for more stories, please visit hackernoon.com. Granting an app permission is only the start of a data trail few people ever see. That information often gets stored, combined, or passed to analytics providers, advertisers, and data brokers long after the original feature is done with it, and the business model behind an app usually explains how much of this happens.
-
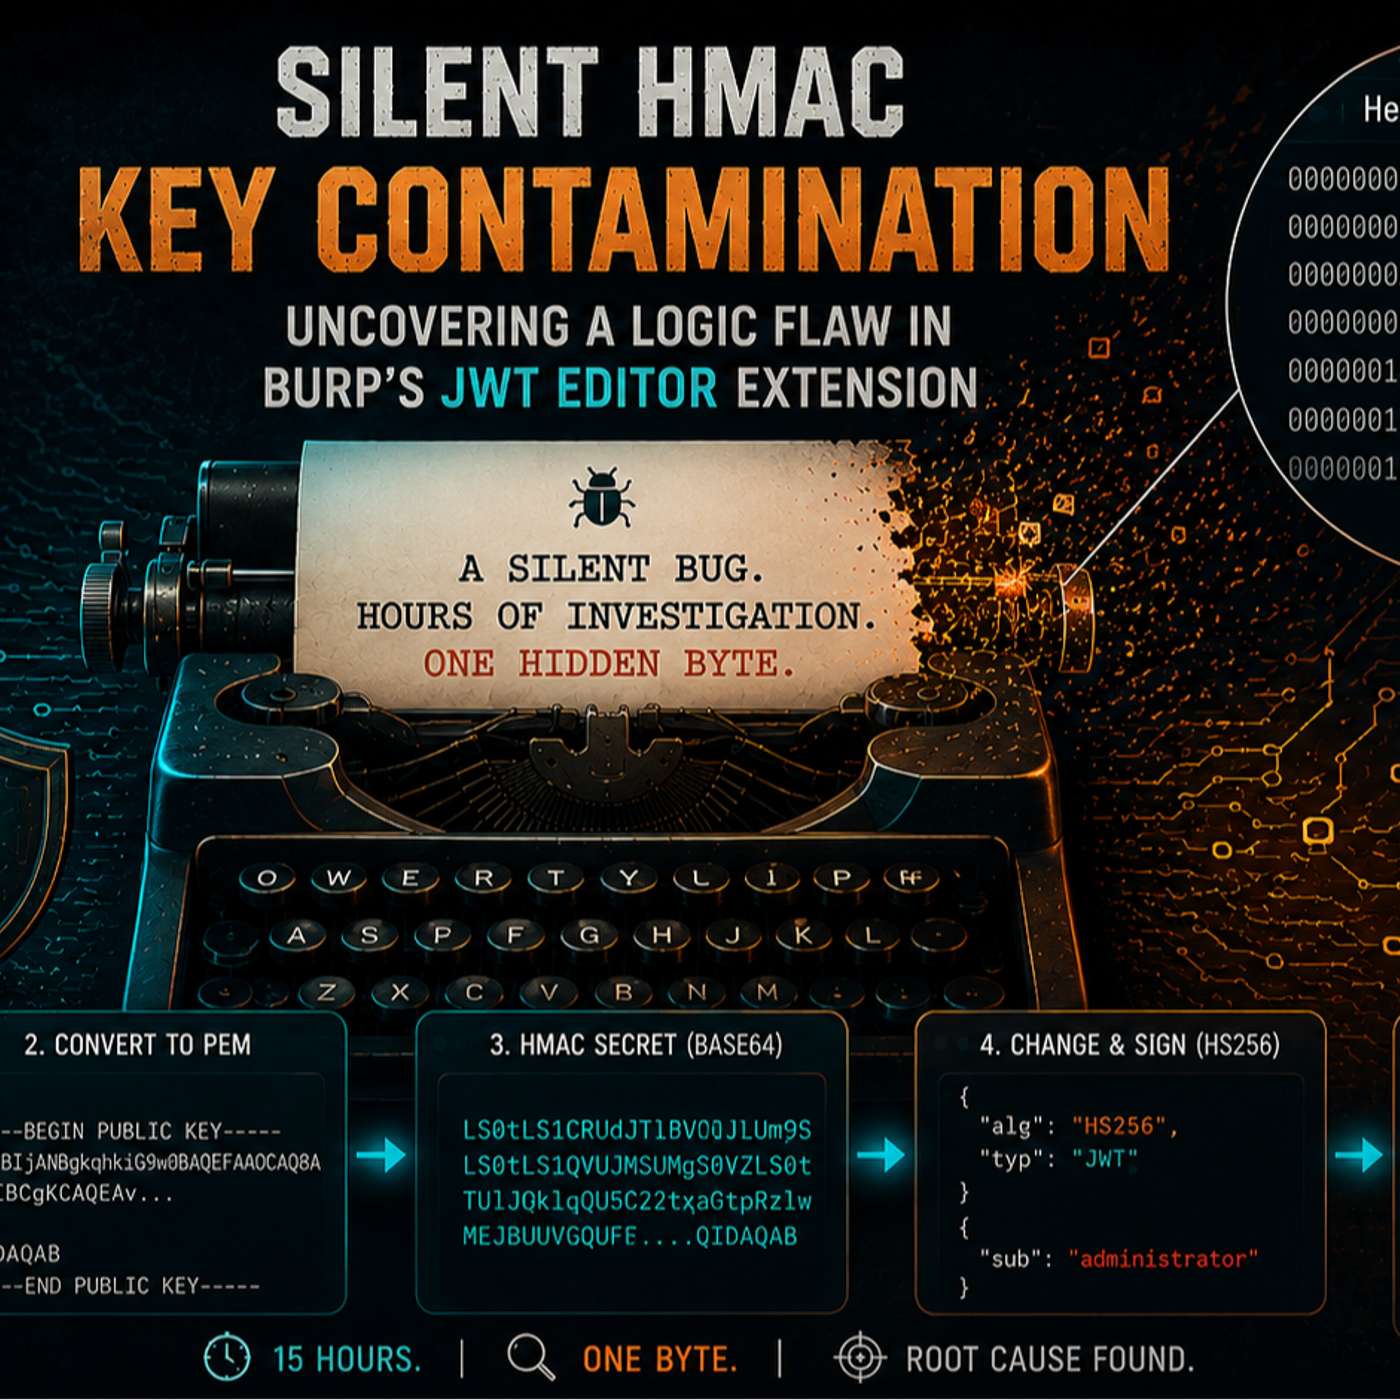 Silent HMAC Key Contamination: Uncovering a Logic Flaw in Burp's JWT Editor Extension 11.09.2026 19minThis story was originally published on HackerNoon at: https://hackernoon.com/silent-hmac-key-contamination-uncovering-a-logic-flaw-in-burps-jwt-editor-extension. JWT Editor was shortlisted for “Best Auth & Access Control” in PortSwigger’s 2026 Burp Suite Extension Awards. This is the story of finding a silent bug inside. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #bug-bounty, #burp-suite, #burp-extensions, #web-security, #infosec, #reverse-engineering, #penetration-testing, #hackernoon-top-story, and more. This story was written by: @rivenx173. Learn more about this writer by checking @rivenx173's about page, and for more stories, please visit hackernoon.com. JWT Editor was shortlisted for “Best Auth & Access Control” in PortSwigger’s 2026 Burp Suite Extension Awards. This is the story of finding a silent bug inside.
-
 Smart Rate Limiting: the Fail-safe Your Bot Vendor Cannot Build for You 10.09.2026 37minThis story was originally published on HackerNoon at: https://hackernoon.com/smart-rate-limiting-the-fail-safe-your-bot-vendor-cannot-build-for-you. Build a forecast-driven, multi-dimensional rate limiter in your stack to catch volumetric bot attacks when commercial vendors lag. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #ai, #prophet, #false-positive-reduction, #bot-attack-mitigation, #forecast-rate-limiting, #adaptive-rate-limiting, #bot-traffic-detection, and more. This story was written by: @brahmbhattspandan. Learn more about this writer by checking @brahmbhattspandan's about page, and for more stories, please visit hackernoon.com. Commercial bot vendors miss sophisticated or fast-moving attacks, leaving a dangerous window of vulnerability. This article details a practical, in-house defense architecture: a forecast-driven, multi-dimensional rate limiter running on familiar libraries like Redis and Prophet. By dynamically modelling normal traffic ceilings and attributing excess to specific behavioral keys, you can safely intercept volumetric scraper and flood attacks at the edge before they impact your origin.
-
 SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path 10.09.2026 8minThis story was originally published on HackerNoon at: https://hackernoon.com/spycloud-2026-identity-threat-report-finds-non-human-identities-are-now-the-leading-path. Ninety-five percent of organizations believe they have visibility into their AI and machine identity exposures, yet only 36% are actually monitoring them. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #spycloud, #cybernewswire, #press-release, #cyber-security-awareness, #spycloud-announcement, #cybercrime, #good-company, and more. This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com.
-
 How TOR Hides You - Onion Routing, Circuits and Hidden Services : Down The Rabbit Hole Part 3 09.09.2026 15minThis story was originally published on HackerNoon at: https://hackernoon.com/how-tor-hides-you-onion-routing-circuits-and-hidden-services-down-the-rabbit-hole-part-3. Hidden services skip the exit node entirely. A rendezvous point splices two anonymous circuits so neither side reveals its IP. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #darkweb, #tor, #privacy, #anonymity, #network-security, #cryptography, #hidden-services, #hackernoon-top-story, and more. This story was written by: @girishatindra. Learn more about this writer by checking @girishatindra's about page, and for more stories, please visit hackernoon.com. TOR is more than just a privacy tool. This part breaks down how TOR actually works under the hood, from building circuits and layered onion encryption to the telescoping key exchange and hidden services that make the dark web possible.
-
 Modernizing Threat Monitoring and Detection Engineering for Ultimate MTTR Reduction 09.09.2026 14minThis story was originally published on HackerNoon at: https://hackernoon.com/modernizing-threat-monitoring-and-detection-engineering-for-ultimate-mttr-reduction. Learn how threat intelligence connects monitoring and detection engineering to help SOC teams reduce alert noise, improve detection, and respond faster. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #threat-intelligence, #soc-threat-monitoring, #soc-operations, #proactive-threat-detection, #mssp-threat-monitoring, #intelligence-driven-soc, #threat-intelligence-feeds, #good-company, and more. This story was written by: @anyrun. Learn more about this writer by checking @anyrun's about page, and for more stories, please visit hackernoon.com. Modern SOCs need more than continuous log collection. This guide explains how threat monitoring, detection engineering, and threat intelligence work together as a continuous operational loop. It covers live intelligence feeds, behavioral threat hunting, YARA rule creation, emerging threat research, and unified workflows that help SOC teams reduce false positives, close detection gaps, improve analyst efficiency, and move from reactive incident response toward proactive defense.
-
 A Green Import Report Is Not a CRM Cutover Test 08.09.2026 11minThis story was originally published on HackerNoon at: https://hackernoon.com/a-green-import-report-is-not-a-crm-cutover-test. Six evidence checks for CRM cutovers: identity, relationships, automation, access, reporting, and recovery. Includes a worked reconciliation example. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #disaster-recovery, #crm-migration, #data-migration, #hubspot, #software-testing, #data-integrity, #enterprise-software, #revops, and more. This story was written by: @mrpratikthakker. Learn more about this writer by checking @mrpratikthakker's about page, and for more stories, please visit hackernoon.com. Matching record totals do not prove a CRM migration is safe. Validate six layers using explicit expected results, record-level reconciliation, negative permission tests, and a recovery rehearsal. Treat the final go-live decision as an evidence review, not a progress update.
-
 Post-Quantum Cryptography and India’s Digital Public Infrastructure 08.09.2026 6minThis story was originally published on HackerNoon at: https://hackernoon.com/post-quantum-cryptography-and-indias-digital-public-infrastructure. India’s Aadhaar, UPI, and DigiLocker systems may need crypto-agility and post-quantum migration as quantum computing risks grow. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #post-quantum-cryptography, #digital-public-infrastructure, #upi-encryption, #digilocker-security, #national-quantum-mission-india, #crypto-agility, #quantum-safe-encryption, #post-quantum-planning, and more. This story was written by: @sam-matrix. Learn more about this writer by checking @sam-matrix's about page, and for more stories, please visit hackernoon.com. The article argues that India’s digital public infrastructure needs early post-quantum planning, including hybrid cryptography, crypto-agile PKI/HSM upgrades, testing, certification, and prioritization of sensitive identity and payment systems.
-
 8 Timer Implementation Patterns for Systems and Network Software 07.09.2026 5minThis story was originally published on HackerNoon at: https://hackernoon.com/8-timer-implementation-patterns-for-systems-and-network-software. A practical guide to system-side timer patterns, from hardware interrupts and OS APIs to timer wheels, heaps, polling, and event loops. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #networking, #system-timers, #timer-architecture, #linux-timers, #network-protocol-timers, #bgp-hold-timers, #event-loop, #kernel-timers, and more. This story was written by: @vijayananda. Learn more about this writer by checking @vijayananda's about page, and for more stories, please visit hackernoon.com. System-side timers can be built in eight different ways — from hardware interrupts and OS APIs to timer wheels, heaps, and event loops. This article breaks down each approach and explains why timer wheels and event-loop-integrated timers (like libevent or epoll/timerfd) are the go-to choices for production networking software handling thousands of concurrent sessions, such as BGP or tunnel keepalives.
-
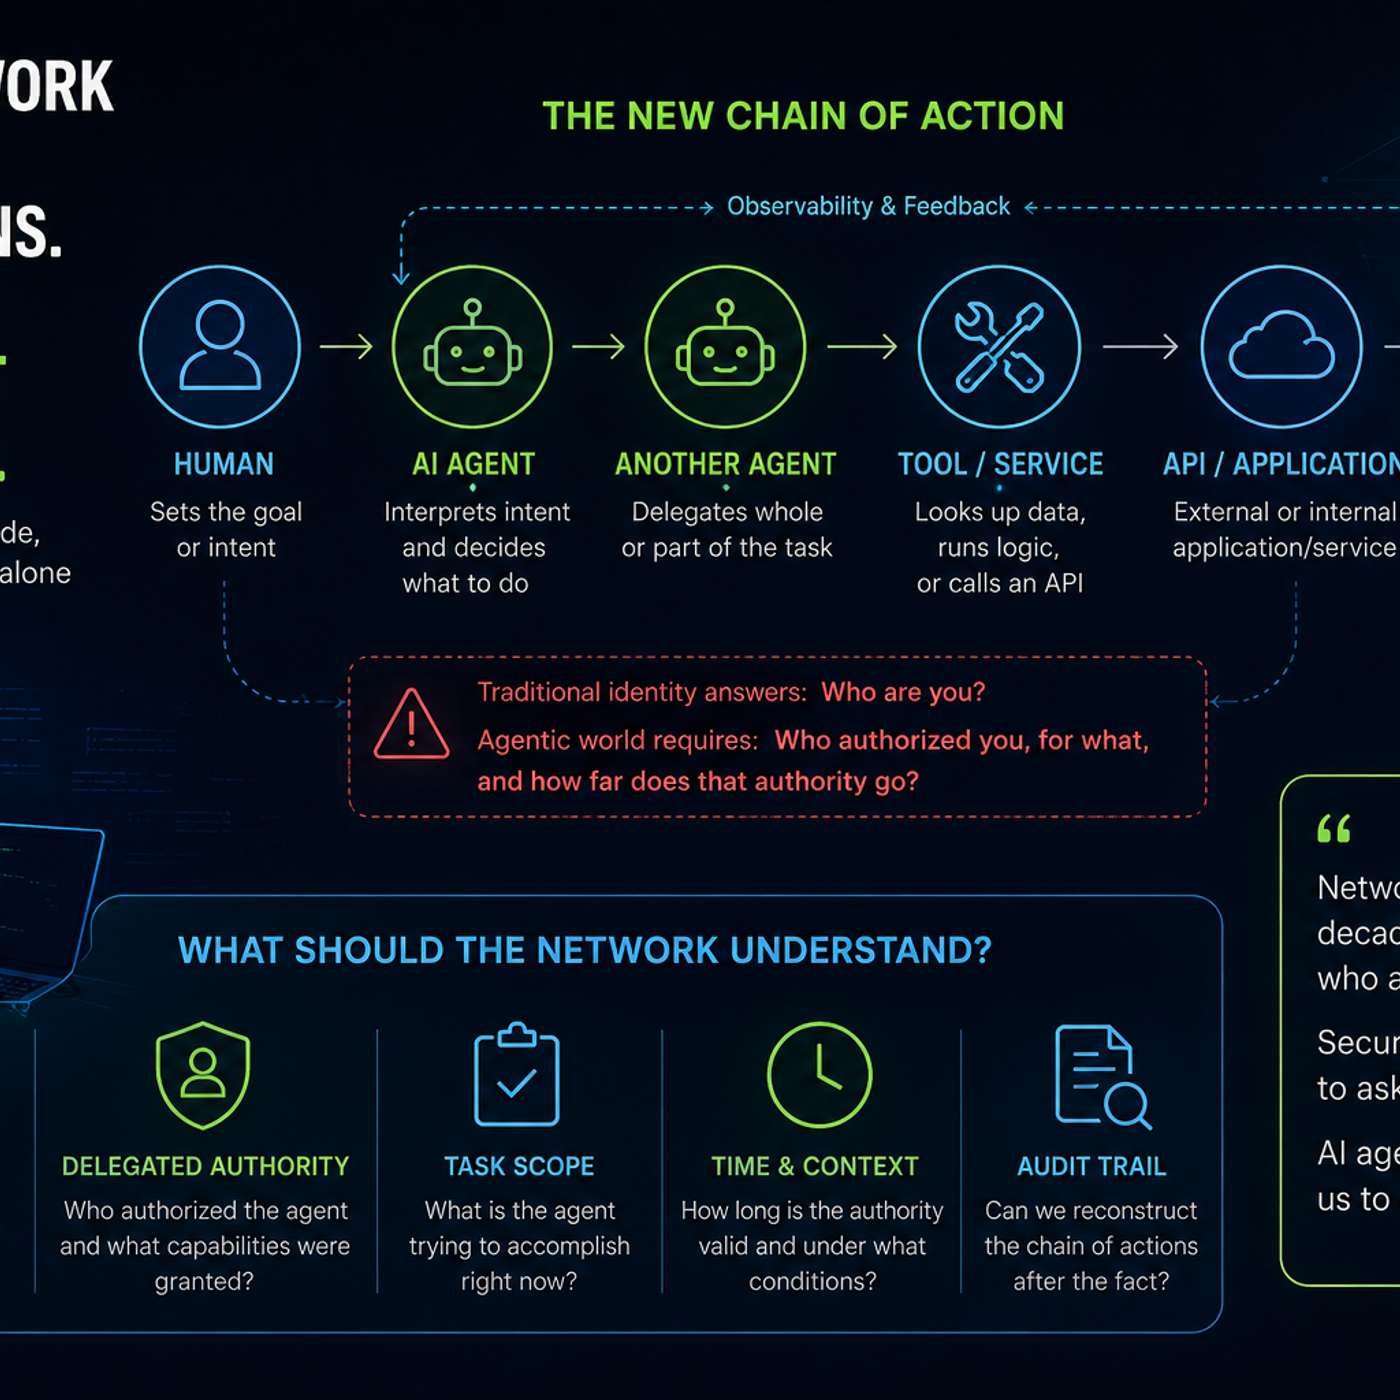 Enterprise Networks Know Who Connected. AI Agents Make the “Why” Harder 07.09.2026 18minThis story was originally published on HackerNoon at: https://hackernoon.com/enterprise-networks-know-who-connected-ai-agents-make-the-why-harder. AI agents complicate enterprise trust because identity alone cannot explain intent, delegated authority, or why a connection happened. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #networking, #network-identity, #ai-agents, #zero-trust, #enterprise-security, #ai-observability, #identity-and-access-management, #machine-identity, and more. This story was written by: @kgsr2194. Learn more about this writer by checking @kgsr2194's about page, and for more stories, please visit hackernoon.com. The article argues that AI agents will stretch enterprise identity models. Knowing who an agent is will not be enough; infrastructure will also need context about authority, delegation, task scope, and intent.
-
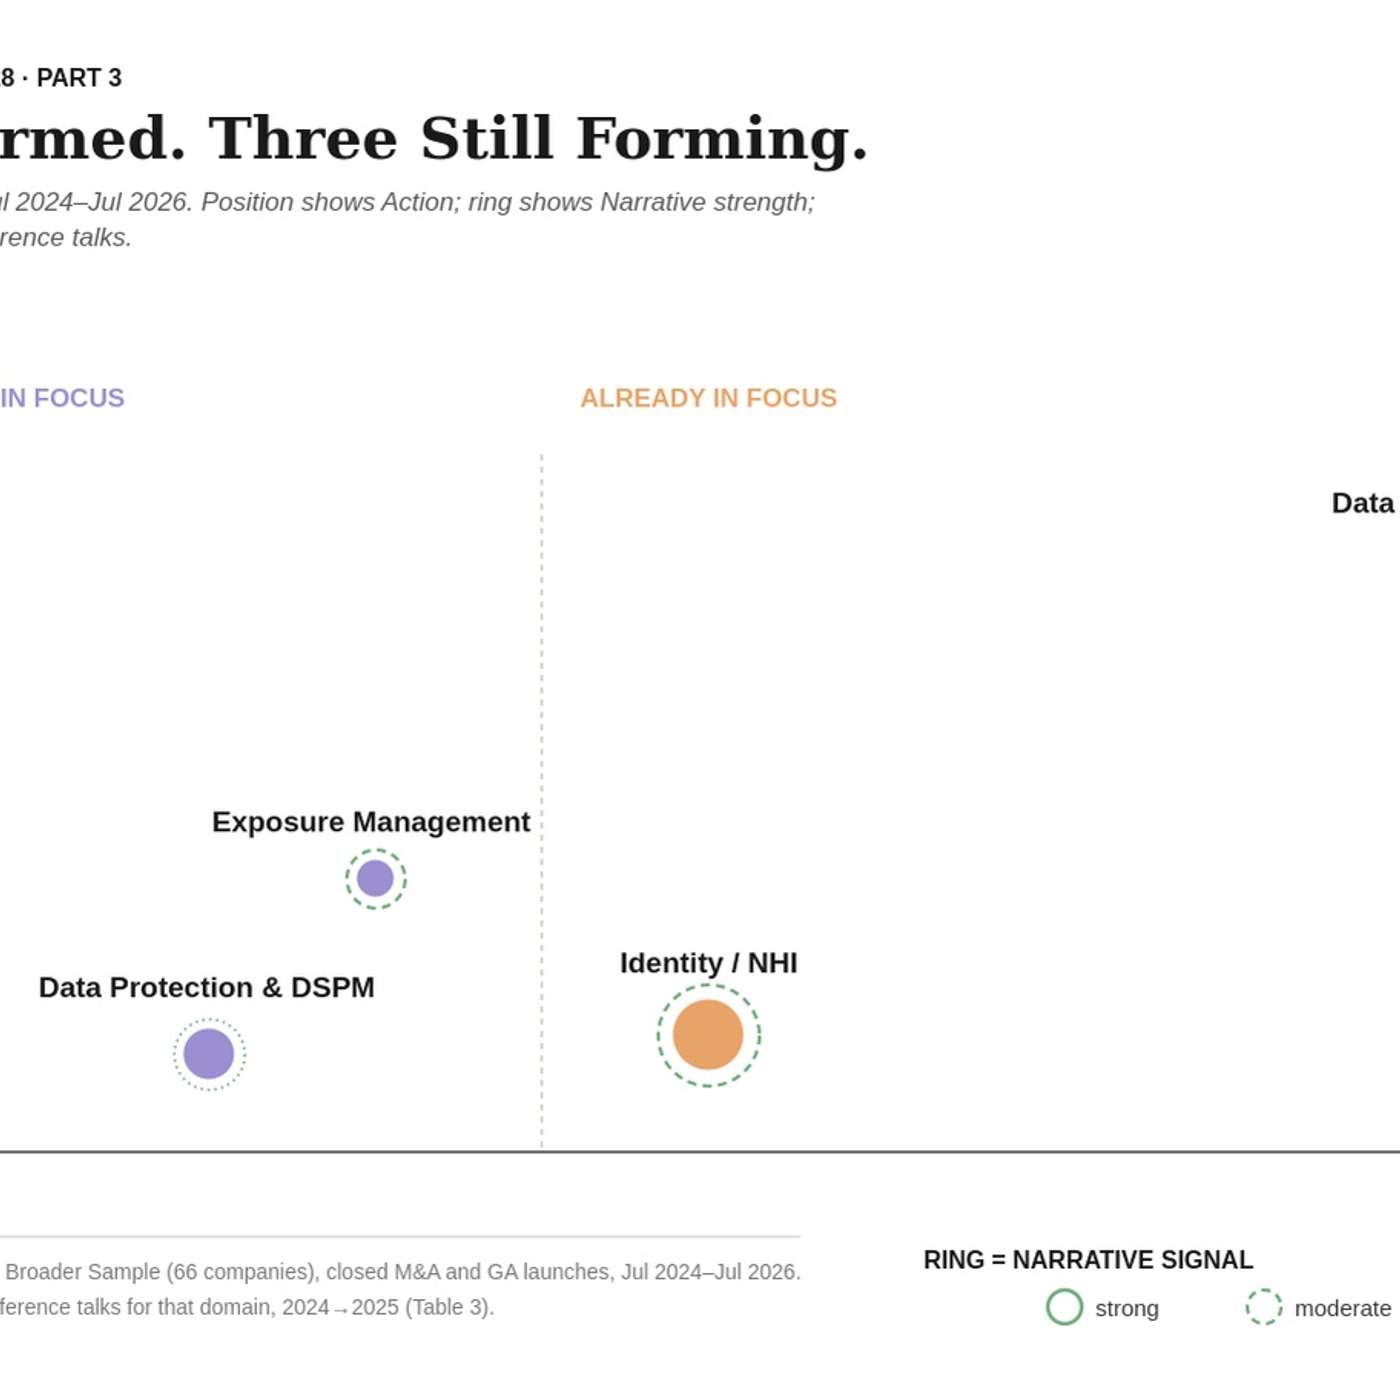 Where the Cybersecurity Market Is Actually Moving in 2026 05.09.2026 49minThis story was originally published on HackerNoon at: https://hackernoon.com/where-the-cybersecurity-market-is-actually-moving-in-2026. A study of 77 cybersecurity vendors reveals how AI Security, Identity, Exposure Management, DSPM, DSA, and PQC are evolving. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #infosecurity, #ai-security, #market-research, #security-architecture, #forecasting, #security, #hackernoon-top-story, and more. This story was written by: @yuriybutuzov. Learn more about this writer by checking @yuriybutuzov's about page, and for more stories, please visit hackernoon.com. A study of 77 cybersecurity vendors reveals how AI Security, Identity, Exposure Management, DSPM, DSA, and PQC are evolving.
-
 Best Autonomous Pentesting Tools for 2026 05.09.2026 15minThis story was originally published on HackerNoon at: https://hackernoon.com/best-autonomous-pentesting-tools-for-2026. Stop guessing with scanners. Discover 7 autonomous pentesting tools that chain real exploits. Compare web, API, and network security leaders for 2026. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #pentesting, #pentesting-tools, #pentesting-ai-tool, #autonomous-pentesting, #cybersecurity, #cyberattacks, #offensive-security, #good-company, and more. This story was written by: @stevebeyatte. Learn more about this writer by checking @stevebeyatte's about page, and for more stories, please visit hackernoon.com. Stop guessing with scanners. Discover 7 autonomous pentesting tools that chain real exploits. Compare web, API, and network security leaders for 2026.
-
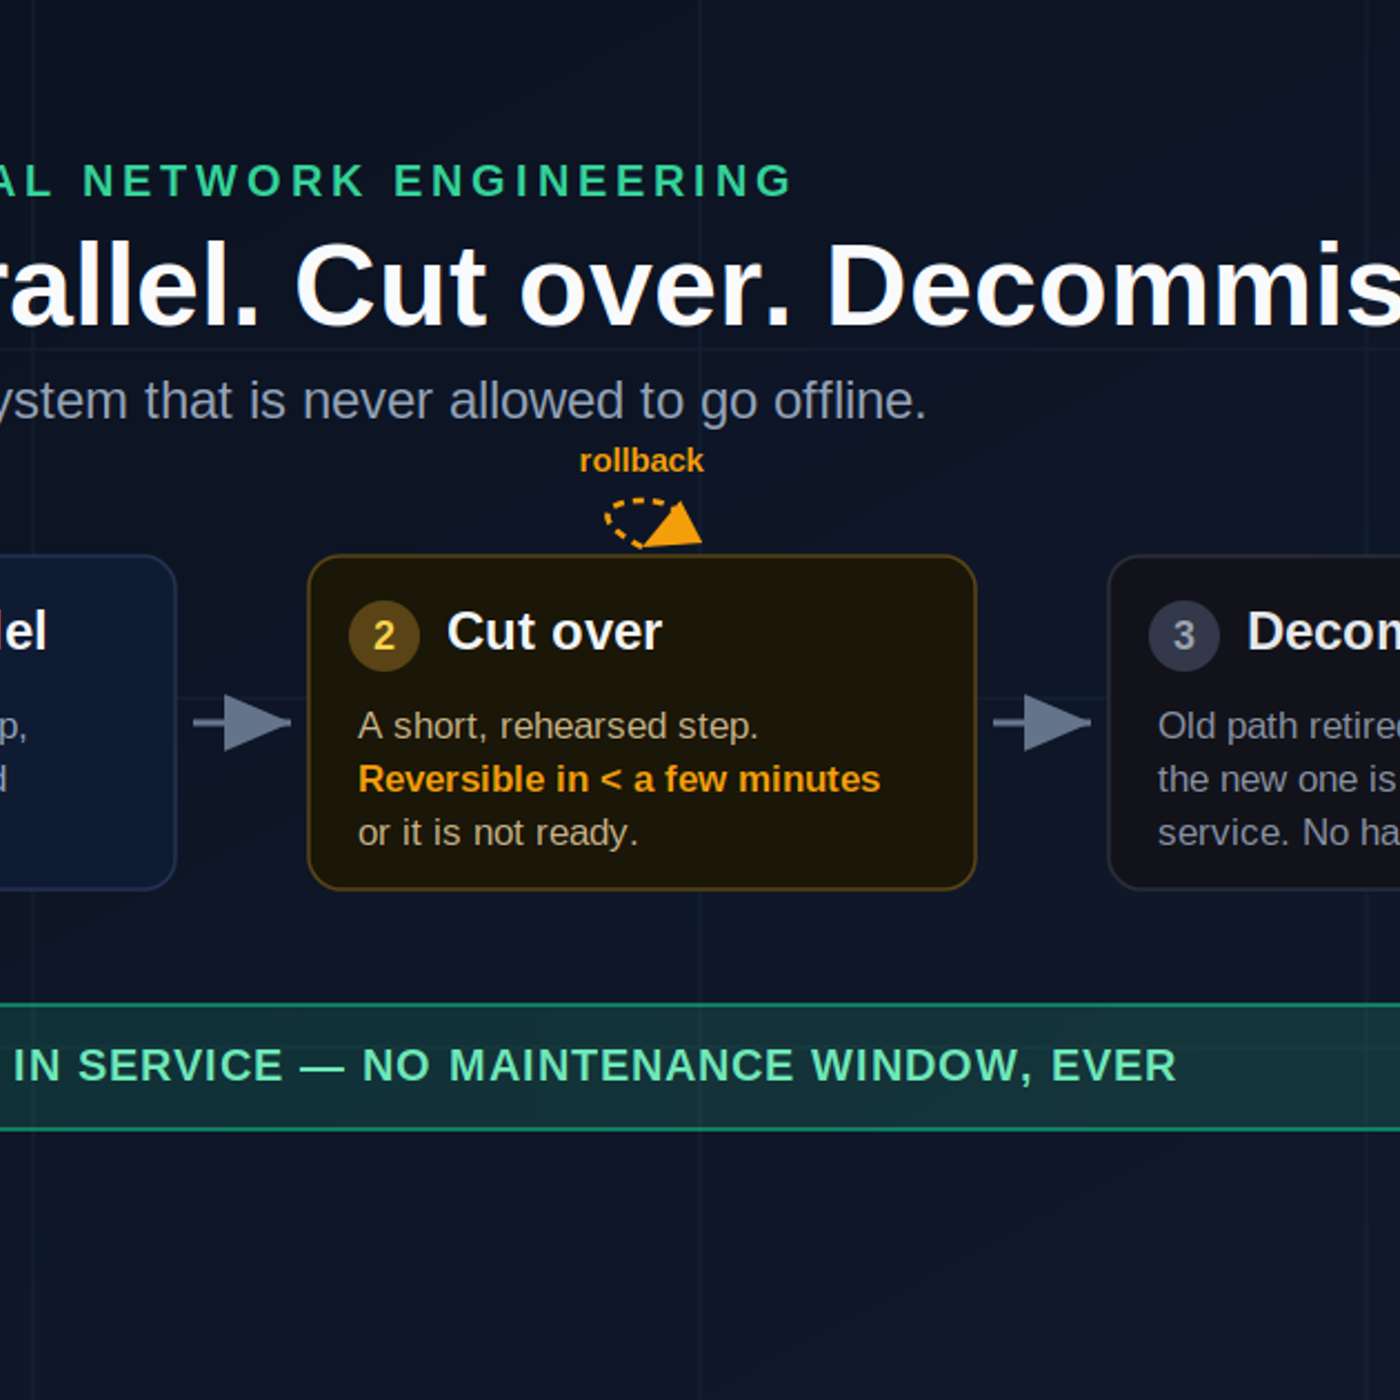 What It Actually Takes to Network a Live System That's Never Allowed to Go Offline 04.09.2026 9minThis story was originally published on HackerNoon at: https://hackernoon.com/what-it-actually-takes-to-network-a-live-system-thats-never-allowed-to-go-offline. Lessons from building transit networks that can never go offline: addressing as a 20-year decision, blast-radius switch design, and testing by breaking things. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #networking, #system-design, #site-reliability-engineering, #infrastructure, #resilience, #building-networks, #public-transit-system, #intercom, and more. This story was written by: @savni. Learn more about this writer by checking @savni's about page, and for more stories, please visit hackernoon.com. I've spent over a decade building networks for a public transit system that's almost never allowed to go offline — surveillance, public address, intercom, and emergency comms running while trains keep moving underneath. That single "no maintenance window" constraint reshapes every decision: addressing schemes become twenty-year commitments, switch configuration becomes a blast-radius problem, and the acceptance test becomes the real deliverable. Here's what mission-critical network engineering actually takes when "down" means a passenger presses a call button and nobody answers.
-
 A Six-Day Intrusion in March Became 3.7 Million Patients in August 04.09.2026 5minThis story was originally published on HackerNoon at: https://hackernoon.com/a-six-day-intrusion-in-march-became-37-million-patients-in-august. CareCloud's breach count went from roughly 350,000 to 3,756,469 — five months after a six-day intrusion. The gap is a data-lineage problem, not a PR one. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #data-breach, #healthcare-security, #incident-response, #cloud-security, #cybersecurity, #healthcare-cybersecurity, #cyber-attack, #hipaa, and more. This story was written by: @nickmarsteller. Learn more about this writer by checking @nickmarsteller's about page, and for more stories, please visit hackernoon.com. CareCloud told federal regulators this week that 3,756,469 people were affected by a March breach of an AWS environment. The figure was first reported as roughly 350,000. The gap between those two numbers is the part worth studying.
Samankaltaiset podcastit


Suosittu maassa
Tämä podcast esiintyy myös näiden maiden podcast-listoilla.

