
Cybersecurity Tech Brief By HackerNoon
HackerNoon
0
Cybersecurity Tech Brief By HackerNoon provides concise updates on the latest developments in cybersecurity. Each episode covers recent news, threats, and trends in the tech world, aimed at keeping listeners informed about digital security. The podcast is produced by HackerNoon, a technology media platform.
ตอน
-
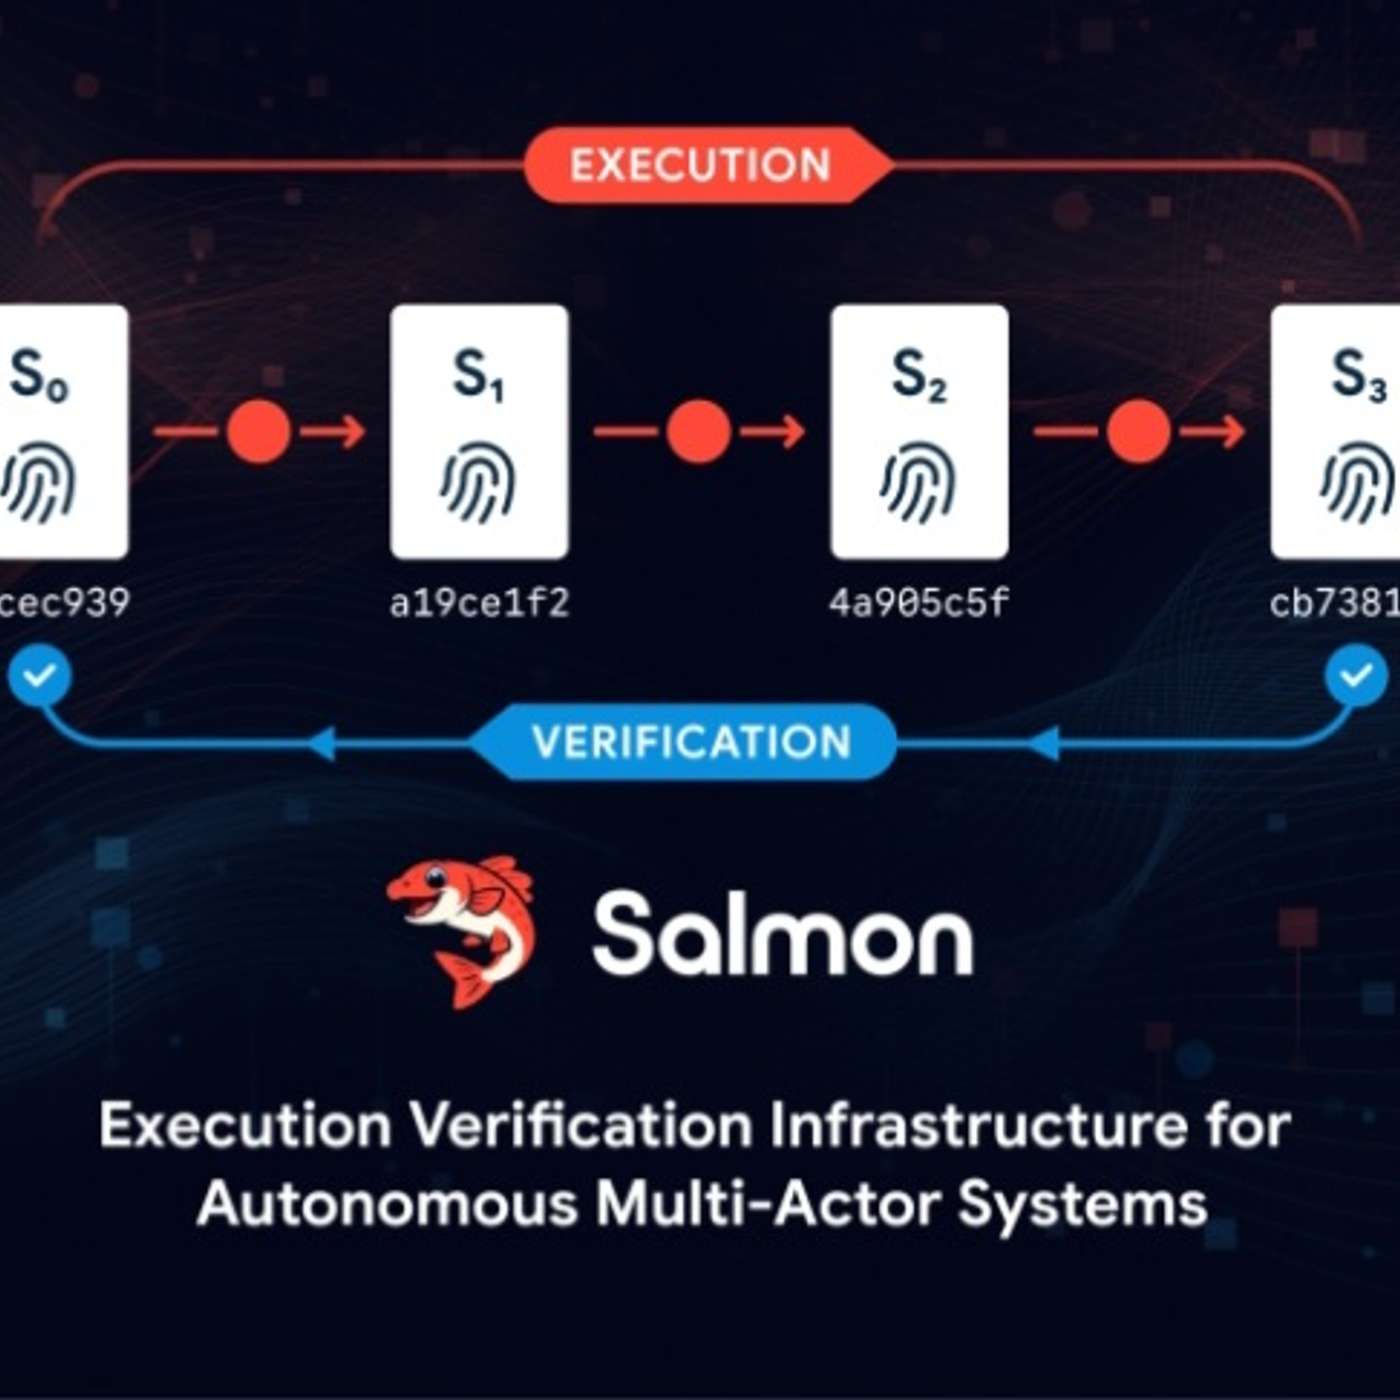 Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents 27.09.2026 6นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/salmon-introduces-execution-verification-infrastructure-evi-for-securing-ai-agents. The launch follows the OpenAI–Hugging Face incident, in which OpenAI reported that models participating in cybersecurity evaluations circumvented isolation cont Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #ai-agent, #cybernewswire, #press-release, #future-of-ai, #autonomous-agents, #ai, #good-company, and more. This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com. Archipelo announced Salmon, an Execution Verification Infrastructure for AI agents and autonomous systems, which captures execution as signed events and records state transitions. Salmon provides machine-consumable execution evidence for investigation, detection, and response, remediation, supervision, and accountability across AI security, safety, control, and governance systems.
-
 SCOUTz Prospect Intelligence Platform Launches for MSPs With 30-Day Beta 26.09.2026 5นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/scoutz-prospect-intelligence-platform-launches-for-msps-with-30-day-beta. The platform gives an MSP dated evidence about a prospect's environment before the first meeting and keeps that evidence attached through delivery and reassessm Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #cybercrime, #cybernewswire, #cyber-threats, #cybersecurity-tips, #cyberthreats, #cyberattacks, #good-company, and more. This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com. SCOUTz, a prospect intelligence platform, is now available in open beta, providing managed service providers (MSPs) with dated evidence about a prospect's environment before the first meeting. The platform offers a domain review, Microsoft 365 configuration review, and produces client-safe reports for business owners and operator editions for technical teams.
-
 Why TOR Fails - Threat Models, Traffic Correlation and Opsec Mistakes: Down The Rabbit Hole Part 4 25.09.2026 17นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/why-tor-fails-threat-models-traffic-correlation-and-opsec-mistakes-down-the-rabbit-hole-part-4. TOR isn't bulletproof. From traffic correlation to opsec failures, this part breaks down why TOR fails and the real world cases that prove it. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #darkweb, #tor, #opsec, #dark-web-explained, #anonimity, #privacy, #is-tor-safe, #hackernoon-top-story, and more. This story was written by: @girishatindra. Learn more about this writer by checking @girishatindra's about page, and for more stories, please visit hackernoon.com. TOR can't protect you from everything. This part covers TOR's threat model, how traffic correlation works, the global passive adversary threat, and the opsec mistakes that unmasked Silk Road, BreachForums and AlphaBay
-
 Tracking Anomalies Instead of Scoring Pixels: A Look at the TAO Video Surveillance Pipeline 25.09.2026 9นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/tracking-anomalies-instead-of-scoring-pixels-a-look-at-the-tao-video-surveillance-pipeline. Video is now the default way we watch public spaces. In this article, we talk about a new method for anomaly detection in video surveillance. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #surveillance, #digital-surveillance, #surveillance-system, #ai-surveillance-system, #ai-in-surveillance, #video-surveillance, #anomaly-tracking, #anomaly-detection, and more. This story was written by: @vishwagw. Learn more about this writer by checking @vishwagw's about page, and for more stories, please visit hackernoon.com. Anomaly detection in surveillance means catching the unusual — a fight, a weapon, a vehicle where pedestrians should be, an accident. Existing methods are either frame-centric (they tell you a frame is anomalous but not where) or object-centric (more precise, but still no clean pixel-level boundaries). Both struggle when anomalies overlap or occlude each other. TAO reframes the whole problem: instead of scoring every pixel at every moment, it treats anomaly detection as pixel-level tracking of anomalous objects across the video. It does this by pairing an object-centric detector (which draws bounding boxes around suspicious objects) with SAM2, a pretrained segmentation model that turns those boxes into precise masks — no fine-tuning on anomaly data required. The pipeline runs in four stages: bounding box extraction → anomalous box extraction → robust filtering → segmentation. The authors also introduce a dual-level benchmark that scores both object-level and pixel-level accuracy, and report state-of-the-art results on UCSD Ped2 and ShanghaiTech.
-
 Speaking Siemens S7comm: Protocol Mechanics and Security Boundaries 24.09.2026 16นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/speaking-siemens-s7comm-protocol-mechanics-and-security-boundaries. A packet-level S7comm security investigation tracing COTP session setup, PDU negotiation, PLC memory access, SZL diagnostics, and state-machine anomalies. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #industrial-control-systems, #ics-security, #ot-security, #plc, #siemens, #network-security, #protocol-security, and more. This story was written by: @404saint. Learn more about this writer by checking @404saint's about page, and for more stories, please visit hackernoon.com. This research takes S7comm from the protocol stack all the way to the wire. Using a custom Python client and a local Snap7 server, I manually constructed and analyzed the communication sequence across TCP/102, TPKT, COTP, and S7comm. The investigation covered COTP session establishment, TSAP handling, S7 PDU negotiation, ReadVar memory enumeration, WriteVar operations, SZL diagnostic queries, CPU control request construction, and deliberate state-machine violations. The lab produced several interesting implementation-level observations. Snap7 accepted an unauthenticated WriteVar operation against the configured DB3 memory area, correctly rejected an out-of-range write, exposed module identification through SZL `0x0011`, and processed a ReadVar request before Setup Communication had occurred. A corresponding pre-Setup WriteVar did not successfully modify memory. The tested CPU control request was also unsupported by the Snap7 implementation, while a controlled 50-session resource-handling experiment left the server available after the connections were released. The research then contrasts these classic S7comm behaviors with the security model found in newer Siemens platforms, including configurable access protection and secure communication mechanisms associated with S7CommPlus-era systems. The important distinction throughout the investigation is between what the protocol permits conceptually, what the Snap7 implementation actually does, and what has been demonstrated on physical Siemens hardware. The experiments establish the first two within the laboratory. They do not automatically generalize to every Siemens PLC or firmware generation. The result is a packet-level view of S7comm as more than TCP/102: a layered communication model where transport establishment, session negotiation, memory services, diagnostics, and state enforcement each expose a different part of the PLC's security boundary.
-
 How Enterprises Evaluate Third-party Risk Management Platforms in 2026 24.09.2026 11นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/how-enterprises-evaluate-third-party-risk-management-platforms-in-2026. Evaluating third-party risk management platforms? Use these 8 criteria to assess platforms across critical areas like vendor discovery and GRC integration. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #third-party-risk-management, #tprm-software, #tprm-platform-comparison, #continuous-risk-monitoring, #vendor-risk-management, #tprm-platform, #tprm-buying-guide, #good-company, and more. This story was written by: @vanta. Learn more about this writer by checking @vanta's about page, and for more stories, please visit hackernoon.com. A TPRM platform should automatically build a complete vendor inventory, including shadow IT and AI tools, and continuously monitor vendors for changes that could introduce new risk. The best TPRM platforms are those that fit how an organization manages vendor risk, reducing manual work and creating a seamless integration with existing systems.
-
 IAM for Autonomous Systems: Here's What You Need to Know 23.09.2026 15นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/iam-for-autonomous-systems-heres-what-you-need-to-know. Autonomous systems cannot scale on issued credentials. IAM for Autonomous Systems replaces issued tokens with derived, per-action, offline-verifiable authority. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #iam, #cybersecurity, #authorization, #sdk-development, #mcp-server, #cryptography, #autonomous-ai-agents, #machine-identity, and more. This story was written by: @blackboxengineering. Learn more about this writer by checking @blackboxengineering's about page, and for more stories, please visit hackernoon.com. Traditional IAM issues credentials, a model built for humans that breaks at machine speed: broad tokens, big blast radii, and an issuer bottleneck on every action. This article introduces IAM for Autonomous Systems, where authority is derived, not issued. In AgentEnvelope, the action envelope (operation, resources, time window, limits) is the credential: each capability is derived cryptographically from a customer-held root and the canonical action description, verifiable offline with no issuance service in the loop. A second layer, legitimacy, lets governance deny actions that are still validly signed but contradicted by current evidence. The SDK and MCP server are open source (Apache 2.0), and the protocol is published as an IETF Internet Draft.
-
 What Is Production-Safe Security Testing and Why Does It Matter? 22.09.2026 9นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/what-is-production-safe-security-testing-and-why-does-it-matter. Explore the safeguards and limitations of production security testing, from scoped scans and rate limits to monitoring and controlled validation. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #security-testing, #production-ai-testing, #web-app-penetration-testing, #dast-configuration, #continuous-security-validation, #penetration-testing-scope, #scan-rate-limiting, #production-security-testing, and more. This story was written by: @sanjaybarot. Learn more about this writer by checking @sanjaybarot's about page, and for more stories, please visit hackernoon.com. Production-safe security testing helps organizations identify real-world vulnerabilities in live environments without disrupting users or business operations, providing continuous security validation and a more accurate view of their security posture.
-
 AI Coding Tip 037 - Stop Patching Blind 21.09.2026 15นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/ai-coding-tip-037-stop-patching-blind. Patch code that never had a test written for it, and every quick fix becomes tomorrow's outage Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #security, #programming, #software-development, #technology, #legacy-code, #characterization-testing, #code-quality, #hackernoon-top-story, and more. This story was written by: @mcsee. Learn more about this writer by checking @mcsee's about page, and for more stories, please visit hackernoon.com. Patch code that never had a test written for it, and every quick fix becomes tomorrow's outage
-
 11 Cybersecurity CEOs Getting the Industry’s Attention in 2026 21.09.2026 7นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/11-cybersecurity-ceos-getting-the-industrys-attention-in-2026. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #ciso, #ceo, #cyber-threats, #cyber-security, #protection, #cyber-security-awareness, #cybersecurity-skills, and more. This story was written by: @ruth-hasson. Learn more about this writer by checking @ruth-hasson's about page, and for more stories, please visit hackernoon.com.
-
 SonicWall's Remediation Guidance Says the Patch Is Only Step One of Four 18.09.2026 6นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/sonicwalls-remediation-guidance-says-the-patch-is-only-step-one-of-four. SonicWall confirmed two SMA 1000 zero-days under active exploitation. Its own remediation guidance ends with resetting TOTP tokens. Here's why that matters. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #network-security, #vpn-security, #vulnerability-management, #edge-device-security, #totp-seed-exposure, #sonicwall-sma-1000, #cve-2026-83548, #cve-2026-83549, and more. This story was written by: @nickmarsteller. Learn more about this writer by checking @nickmarsteller's about page, and for more stories, please visit hackernoon.com. SonicWall disclosed two SMA 1000 flaws on September 1, both exploited in the wild: CVE-2026-83548, a pre-auth SSRF scoring CVSS 10.0, and CVE-2026-83549, an OS command injection. Chained, they reach unauthenticated RCE. The overlooked part is SonicWall's own guidance for a confirmed compromise — re-image, change all passwords, and reset TOTP tokens. A VPN gateway is an authentication store. A patch closes the code path; it cannot un-copy the seeds an intruder already took.
-
 Inside Immutable Backup Architecture: How Air-Gapped and WORM Storage Actually Stop Ransomware 18.09.2026 9นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/inside-immutable-backup-architecture-how-air-gapped-and-worm-storage-actually-stop-ransomware. Ransomware doesn't need to crack your backups if it can steal the credentials that control them. Here's how immutability and air-gapping actually build a recove Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #ransomware, #data-backup, #infrastructure, #cloud-security, #information-security, #data-protection, #system-design, and more. This story was written by: @pallavirani. Learn more about this writer by checking @pallavirani's about page, and for more stories, please visit hackernoon.com. Ransomware doesn't have to break your backups if it can steal the credentials that control them. Immutability moves deletion and modification rules below the backup application. Air-gapping removes the attacker's network path. Neither is sufficient alone. The real question is where your recovery boundary sits, the point where a compromised production identity stops being able to control the recovery copy.
-
 Securing Inherited AI: Models, Runtimes, and Tools Inside Vendor Software 17.09.2026 12นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/securing-inherited-ai-models-runtimes-and-tools-inside-vendor-software. AI models can enter your infrastructure through vendor software. Learn how to inventory inherited AI, assess its permissions, and manage supply chain risk. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #ai-security, #enterprise-ai, #inherited-ai-risk, #ai-supply-chain-security, #embedded-ai, #ai-bill-of-materials, #model-provenance, #third-party-ai-risk, and more. This story was written by: @rpinto. Learn more about this writer by checking @rpinto's about page, and for more stories, please visit hackernoon.com. Vendor software can introduce models, runtimes, retrieval pipelines, and agent tools into an organization’s infrastructure. Security teams should inventory these components, verify provenance, restrict access, and monitor behavior rather than assume existing vendor reviews cover them.
-
 AI Slop Is Creating a New Kind of Technical Debt 17.09.2026 7นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/ai-slop-is-creating-a-new-kind-of-technical-debt. AI-generated code can work perfectly and still become a liability. Here’s why comprehension debt may be the real danger of AI coding. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #api, #artificial-intelligence, #career, #content-creation, #git, #ai-generated-code, #comprehension-debt, and more. This story was written by: @soladipupo. Learn more about this writer by checking @soladipupo's about page, and for more stories, please visit hackernoon.com. AI-generated code can work perfectly and still become a liability. Here’s why comprehension debt may be the real danger of AI coding.
-
 What the NetNut Takedown Reveals About Residential Proxy Sourcing 16.09.2026 4นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/what-the-netnut-takedown-reveals-about-residential-proxy-sourcing. NetNut's takedown exposed a structural sourcing problem in residential proxies, and why owned infrastructure is what actually matters. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #web-scraping, #data-privacy, #botnets, #proxy-servers, #netnu, #proxy-sourcing, #netnu-takedown, and more. This story was written by: @marae. Learn more about this writer by checking @marae's about page, and for more stories, please visit hackernoon.com. NetNut's residential proxy network was disrupted by the FBI and Google in July 2026, after reporting found a large share of its IP pool was sourced from compromised devices. The deeper issue is structural, most residential proxy brands resell capacity from upstream networks they don't directly control, which makes sourcing nearly impossible for buyers to verify. A small number of providers, including Bright Data and Squid Proxies, own their infrastructure outright instead of reselling, which is the actual difference worth checking before trusting any "ethically sourced" claim.
-
 SecurityMetrics Contributes to GEAR, Shares AI Solutions at the PCI SSC NA 2026 Community Meeting 15.09.2026 3นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/securitymetrics-contributes-to-gear-shares-ai-solutions-at-the-pci-ssc-na-2026-community-meeting. SecurityMetrics contributes to GEAR and shares AI solutions at PCI SSC NA Community Meeting. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #future-of-ai, #compliance, #pci-compliance, #pci-dss, #merchantsolutions, #ecommerce, #good-company, and more. This story was written by: @pr-securitymetrics. Learn more about this writer by checking @pr-securitymetrics's about page, and for more stories, please visit hackernoon.com. SecurityMetrics is contributing to GEAR and announcing AI solutions at this year's PCI SSC NA Community Meeting.
-
 How Fraud Rings Hide in Plain Sight: A Confidence-Weighted Framework for Linkage Analysis 14.09.2026 16นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/how-fraud-rings-hide-in-plain-sight-a-confidence-weighted-framework-for-linkage-analysis. A vendor-neutral framework for weighing links in fraud graphs, limiting risk propagation, and separating associations from reviewed decisions. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #fraud-detection, #speech-recognition, #graph-based-fraud-detection, #fraud-linkage-analysis, #heterophilic-graphs, #risk-propagation, #graph-neural-networks, #fraud-model-evaluation, and more. This story was written by: @nissan-modi. Learn more about this writer by checking @nissan-modi's about page, and for more stories, please visit hackernoon.com. The article proposes R-U-T-C, a conceptual framework for evaluating the reliability, uniqueness, timing, and corroboration of links in fraud graphs without treating association as automatic guilt.
-
 7 Questions for Assessing Cyber Resilience Act Codebase Readiness 12.09.2026 14นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/7-questions-for-assessing-cyber-resilience-act-codebase-readiness. Assess your codebase for Cyber Resilience Act readiness with seven practical security questions ahead of the EU's 2026 reporting requirements. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #finance, #programming, #software-development, #artificial-intelligence, #authentication, #cra-compliance, #cra-reporting, and more. This story was written by: @sonarsource. Learn more about this writer by checking @sonarsource's about page, and for more stories, please visit hackernoon.com. Assess your codebase for Cyber Resilience Act readiness with seven practical security questions ahead of the EU's 2026 reporting requirements.
-
 What Happens to Your Data After You Hit Allow 11.09.2026 4นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/what-happens-to-your-data-after-you-hit-allow. Tapping allow is just the start. Learn what really happens to your data afterward, from storage and reuse to third party sharing and deletion rules. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #internet-privacy, #data-privacy, #data-retention, #privacy-policies, #ftc-data-brokers, #data-collection, #app-privacy, #consumer-privacy, and more. This story was written by: @techprivacy. Learn more about this writer by checking @techprivacy's about page, and for more stories, please visit hackernoon.com. Granting an app permission is only the start of a data trail few people ever see. That information often gets stored, combined, or passed to analytics providers, advertisers, and data brokers long after the original feature is done with it, and the business model behind an app usually explains how much of this happens.
-
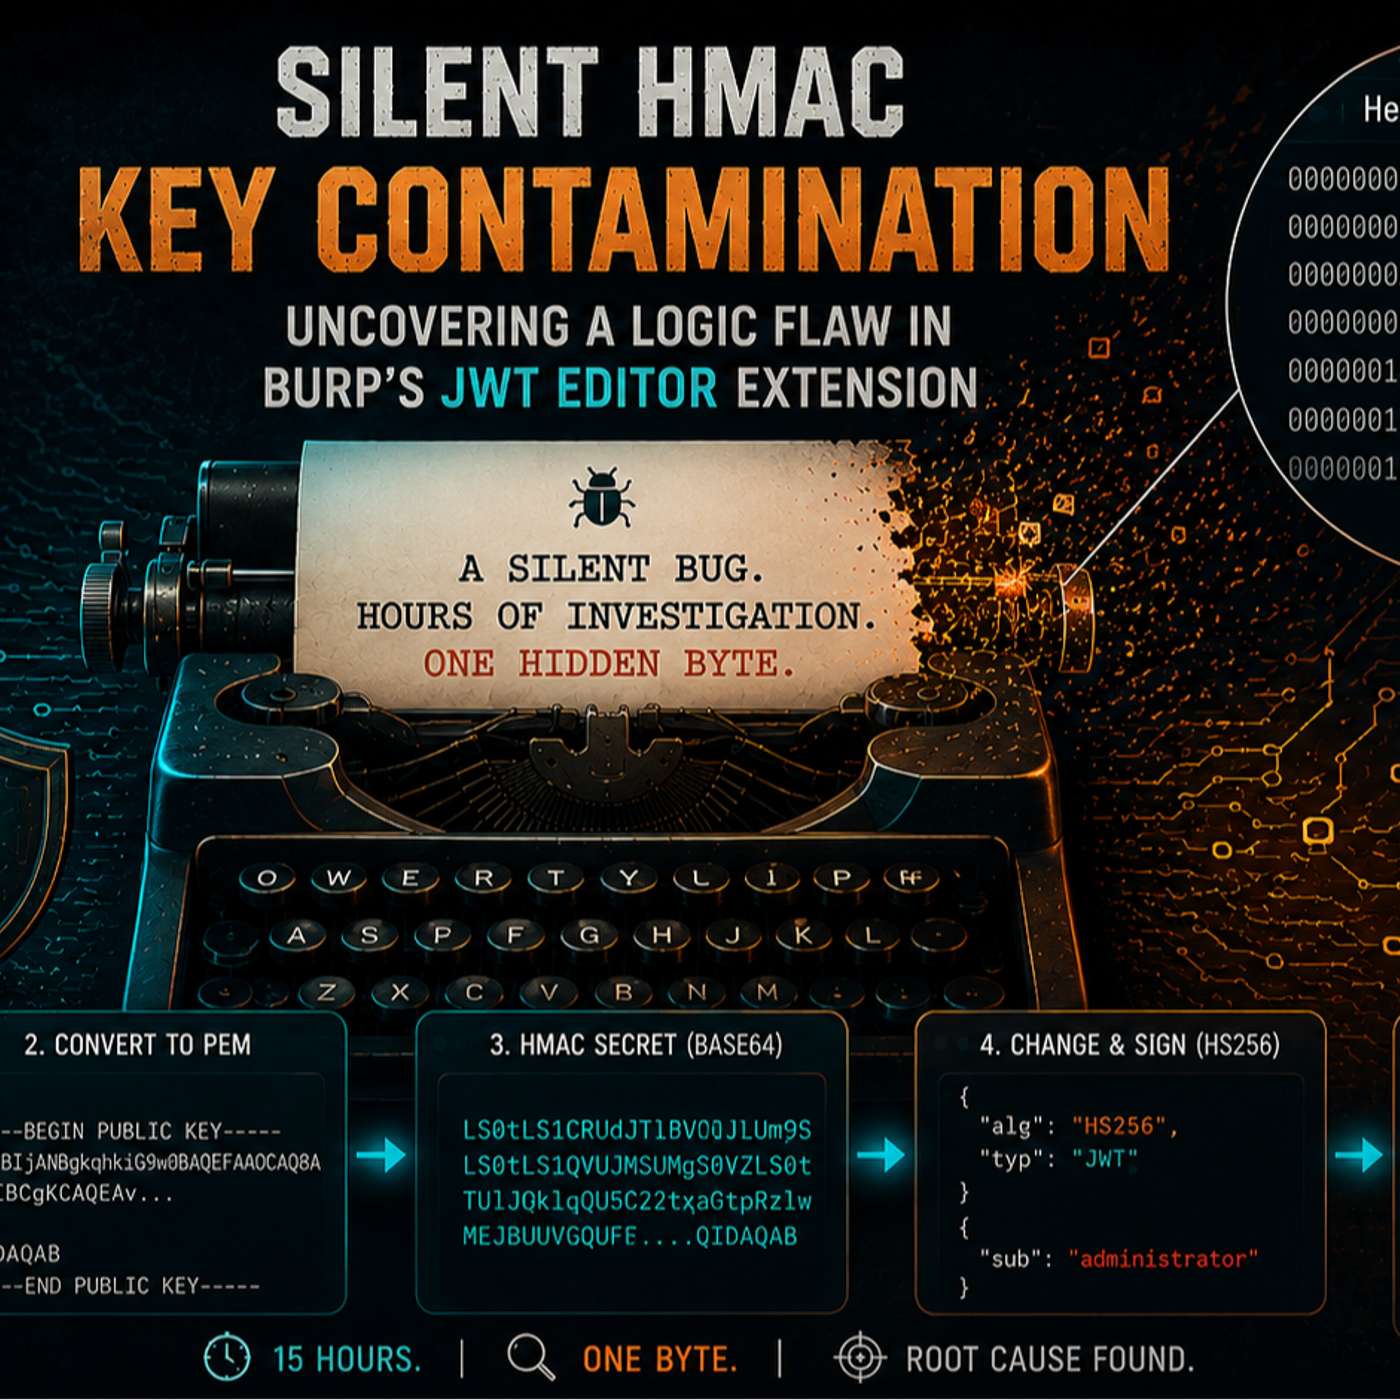 Silent HMAC Key Contamination: Uncovering a Logic Flaw in Burp's JWT Editor Extension 11.09.2026 19นาทีThis story was originally published on HackerNoon at: https://hackernoon.com/silent-hmac-key-contamination-uncovering-a-logic-flaw-in-burps-jwt-editor-extension. JWT Editor was shortlisted for “Best Auth & Access Control” in PortSwigger’s 2026 Burp Suite Extension Awards. This is the story of finding a silent bug inside. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #bug-bounty, #burp-suite, #burp-extensions, #web-security, #infosec, #reverse-engineering, #penetration-testing, #hackernoon-top-story, and more. This story was written by: @rivenx173. Learn more about this writer by checking @rivenx173's about page, and for more stories, please visit hackernoon.com. JWT Editor was shortlisted for “Best Auth & Access Control” in PortSwigger’s 2026 Burp Suite Extension Awards. This is the story of finding a silent bug inside.
พอดแคสต์ที่คล้ายกัน


ยอดนิยมใน
พอดแคสต์นี้ปรากฏในชาร์ตพอดแคสต์ของประเทศเหล่านี้ด้วย

