
Entra.Chat
Merill Fernando
0
Entra Chat is a weekly podcast hosted by Merill Fernando that offers practical insights for Microsoft administrators and security professionals. Each episode features conversations with identity experts who share real-world deployment experiences, as well as Microsoft Entra team members who discuss the features they build. The show covers best practices, implementation strategies, and upcoming capabilities in Microsoft identity solutions. Listeners gain actionable takeaways that can be applied immediately in Microsoft 365, Azure, and Entra environments. The content reflects Merill's personal opinions and is not an official Microsoft publication.
Episodes
-
 Which Passkey Should Your Users Get? The FIDO Alliance CTO on Passkeys and Post-Quantum Cryptography 14.11.2026 44mMicrosoft is moving millions of users off SMS and onto passkeys, and most admins now have to decide which kind of passkey each group of users should get. Nishant Kaushik, CTO of the FIDO Alliance, the industry body behind the passkey standards, explains the three flavours of workforce passkey, how to roll out hardware security keys without repeating the RSA token years, and why passkeys are your best route to the post-quantum cryptography deadlines.Key takeawaysPick the right passkey for each user* Passkeys are about phishing, not passwords. The FIDO Alliance set out to build phishing-resistan...
-
 Free AI Agents, the E7 Bill and AD vs Entra: The Workplace Ninjas US Special 07.11.2026 24mAI agents are arriving in every Microsoft 365 tenant, and the questions admins ask first are what they cost to run and what it costs to secure them. In this Workplace Ninjas US special, four of the event’s speakers answer from the field: Jon Towles, founder of Workplace Ninjas US, Intune and AI tool builder Ugur Koc, Microsoft 365 security MVP Ru Campbell, and Spencer Alessi, the pen tester who defends Active Directory against Merill in the event’s AD vs Entra cage match.Key takeawaysAI agents: cheap to run, not free to secure* Admin agents can run on a laptop. You don’t need Security Compute...
-
 Entra Multi-Tenant App Mistakes Every SaaS Builder and Admin Should Know, with Kelvin Tegelaar 31.10.2026 43mMost SaaS vendors connect to your tenant with one multitenant app and one credential, shared by every customer. Kelvin Tegelaar, founder of CyberDrain and creator of CIPP (used by well over 10,000 MSPs), sees it from both sides, and his verdict is blunt: “This app is dangerous, period.”Recorded on 14 October 2026, one day before the ConnectWise Cloud Backup app’s credential was used to sign in to customer tenants (173 confirmed by Huntress).Key takeawaysThe risk: one app, every tenant* One app registration, a service principal in every tenant. The credentials sit on the vendor’s app registrati...
-
 Conditional Access Gaps and the App Back Door, with Brandon Colley 24.10.2026 39mMost Conditional Access gaps aren’t exotic. They come from reading policies the wrong way: as firewall rules with an “allow”, as a list of platforms that seems complete, as an MFA exception for the office that made sense years ago. Brandon Colley has reviewed well over a thousand Conditional Access policies in customer assessments, and the same handful of mistakes come up in tenant after tenant.Once those are fixed, the risk moves. Passkeys, privileged access and Conditional Access put more locks on the front door, the user sign-in. An app that was consented to years ago, holds a client secret...
-
 Stop the Bleeding: Cleaning Up Apps, Secrets and Consent in Microsoft Entra 17.10.2026 50mMost tenants have the same problem: hundreds of app registrations and service principals, client secrets that were set to expire in a hundred years, permission grants nobody remembers approving, and test tenants that were never cleaned up. It’s tempting to start fixing the scariest app on the list. Jeff Sakowicz argues for a different order: stop the problem from growing first, then remove the debt that gives you the most risk reduction for the least disruption.Jeff isn’t describing someone else’s product. He has spent most of his 14 years at Microsoft as a product leader on the Entra applicat...
-
 Stolen Tokens, Agents and Universal CAE: What Global Secure Access Adds to Entra ID 09.10.2026 50mA phished and stolen refresh token is one of the most useful things an attacker can take from your tenant. It is a long-term artifact, which is why so many phishing attempts go after it. Alex Pavlovsky’s answer to that attack is a feature every Entra ID P1 tenant already owns.Compliant network is part of Global Secure Access, and, like source IP restoration, it comes with Entra ID P1. Put the GSA client on your devices, add one Conditional Access policy that blocks access from anywhere outside the All Compliant Network locations named location, and a stolen refresh token or PRT cookie no longe...
-
 Your AI Coding Agent Is Creating Secrets You Don’t Know About 02.10.2026 34mAsk a coding agent to build something that talks to another service and watch what it does. It creates a client secret. Then another one. As Arturo Lucatero puts it, next thing you know you have ten secrets that were created without you knowing about it. At the speed AI is moving, he thinks we could be cleaning up a few million new secrets within six months.That would undo a lot of hard work. Under Microsoft’s Secure Future Initiative, Microsoft spent years removing secrets from its own estate and helping customers do the same with managed identities and workload identity federation. The agent...
-
 Active Directory Security Testing in Maester 2.2 17.09.2026 36mActive Directory is not dead. It is nearly thirty years old, Microsoft is still shipping new capabilities and new telemetry for it, and most of the forests running today will outlive the people currently administering them. What has changed is that you can now test it the same way you test your cloud tenant.Maester, the open-source PowerShell testing framework, added Active Directory coverage: 269 opt-in checks across 19 areas, from users, groups, computers and service principal names through GPO state, DACLs, DNS, trusts, replication and schema. They run against your domain, not your tenant,...
-
 Microsoft Security Architect: Active Directory Is 10x Harder to Defend Than Entra 06.09.2026 59mAt Black Hat USA 2026, Microsoft’s David Weston put three numbers on a slide that anyone still running domain controllers should sit with. The Microsoft Security Response Center went from 80 patches in February to 1,142 at the July Patch Tuesday. The fastest observed breakout time dropped from 98 minutes to 27 seconds. And mean time-to-exploit flipped from 63 days after a patch shipped to seven days before the patch existed.Tarek Dawoud, Lead Architect on the Technical Excellence Team in Microsoft Security, walks Merill through those slides and then draws the conclusion for identity teams in h...
-
 How General Motors Moved 200,000 People to Passkeys 31.08.2026 43mMicrosoft starts making passkeys the default in Microsoft Entra ID on 1 September 2026, and retires Microsoft-provided SMS and voice MFA on 1 February 2027. Every organisation with a large, messy population now has to answer a question that has nothing to do with passkey technology itself: how do you move a hundred thousand real people - office workers, factory floors, call centres and guests - without locking someone out?In this episode, Merill sits down with the person who has already done it. Andrew Cameron is a Distinguished Engineer for Identity and Cybersecurity at General Motors, and he...
-
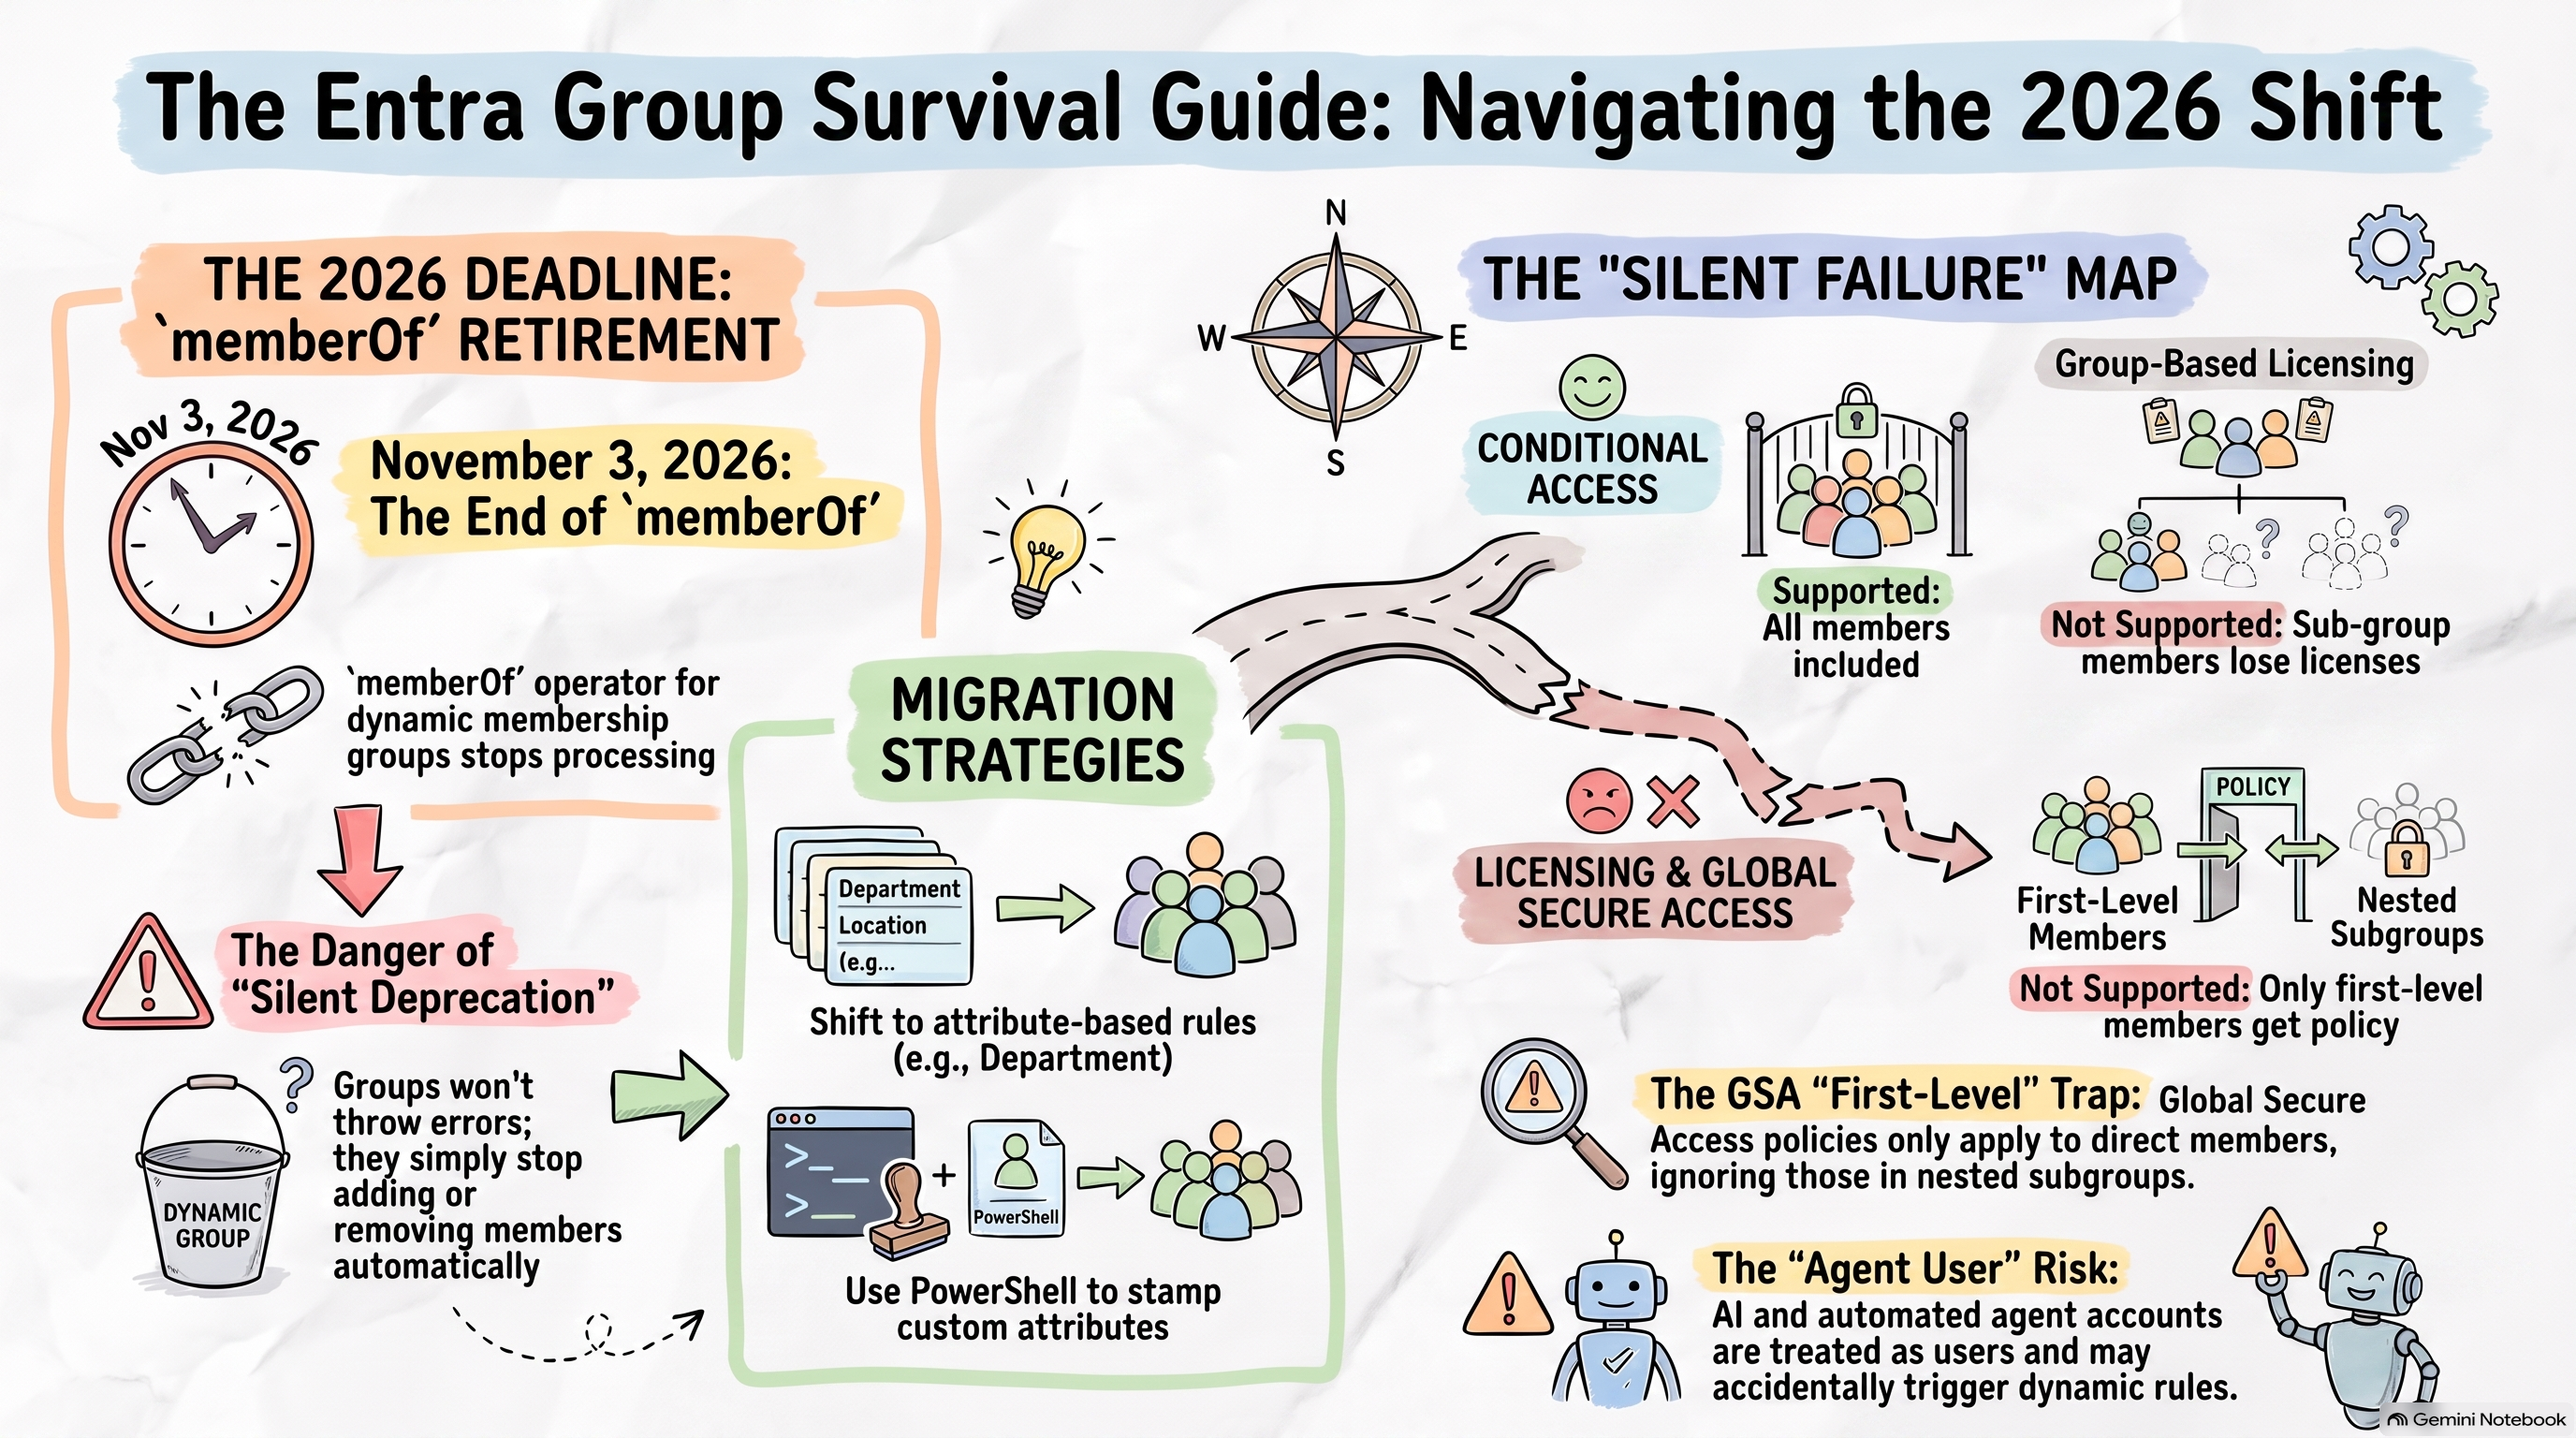 Microsoft Entra memberOf Retirement: What Admins Must Do 25.08.2026 42mOn 3 November 2026, the memberOf operator in Microsoft Entra dynamic membership groups stops working. Nothing errors. Nothing breaks loudly. Every dynamic group, dynamic administrative unit and entitlement management auto-assignment policy that uses it simply freezes in its last known state the people who should be added are not added, and the people who should be removed stay.It was a preview feature for four years. It is in a lot of production tenants.In this episode of Entra.Chat, Merill is joined by three guests for the first time: Gregor Reimling, Chief Azure Technologist at adesso SE and...
-
 Pass-the-Passkey: What Michael Grafnetter's Black Hat Research Means for Entra Admins 17.08.2026 36mPasskeys are phishing-resistant. But that resistance is enforced by your browser, which binds every authentication to the origin that requested it. Skip the browser, and the guarantee weakens.In this episode of Entra.Chat, I spoke with Michael Grafnetter, Principal Security Researcher at SpecterOps and Microsoft MVP, about the Pass-the-Passkey research he presented at Black Hat USA 2026. A family of attacks against passkey implementations across Windows, Microsoft Entra ID, browsers and password managers.Michael starts with the vulnerability chain he reported to Microsoft. Windows was writing...
-
 From SMS MFA to Passkeys: A Practical Microsoft Entra Migration Plan 10.08.2026 53mMicrosoft-managed SMS and voice MFA will stop working on February 1, 2027. That deadline makes passkey planning urgent, but enabling a new authentication method is only the first milestone.In this episode of Entra.Chat, Merill speaks with Jai Maharaj, Product Manager at Microsoft, about the practical journey from legacy MFA to a passwordless Microsoft Entra environment. Jai explains what is actually being retired, why organizations can still use a customer-managed telecom provider, and how passkey profiles support synced and device-bound passkeys for different user personas.The user-experience...
-
 The Ultimate Microsoft Entra Global Secure Access Migration Guide 03.08.2026 48mAn Entra GSA migration should not mean throwing away years of useful SSE policy work and rebuilding every application, segment, and rule by hand.Existing configuration carries hard-won intent: which populations need access, which destinations should be blocked, and which exceptions keep the business running. Migrate2GSA creates a path to preserve the useful parts while making the migration a deliberate cleanup opportunity.In this episode of Entra.Chat, I spoke with Andres Canello, Principal Product Manager at Microsoft and creator of Migrate2GSA. Andres demonstrates how the open-source toolkit...
-
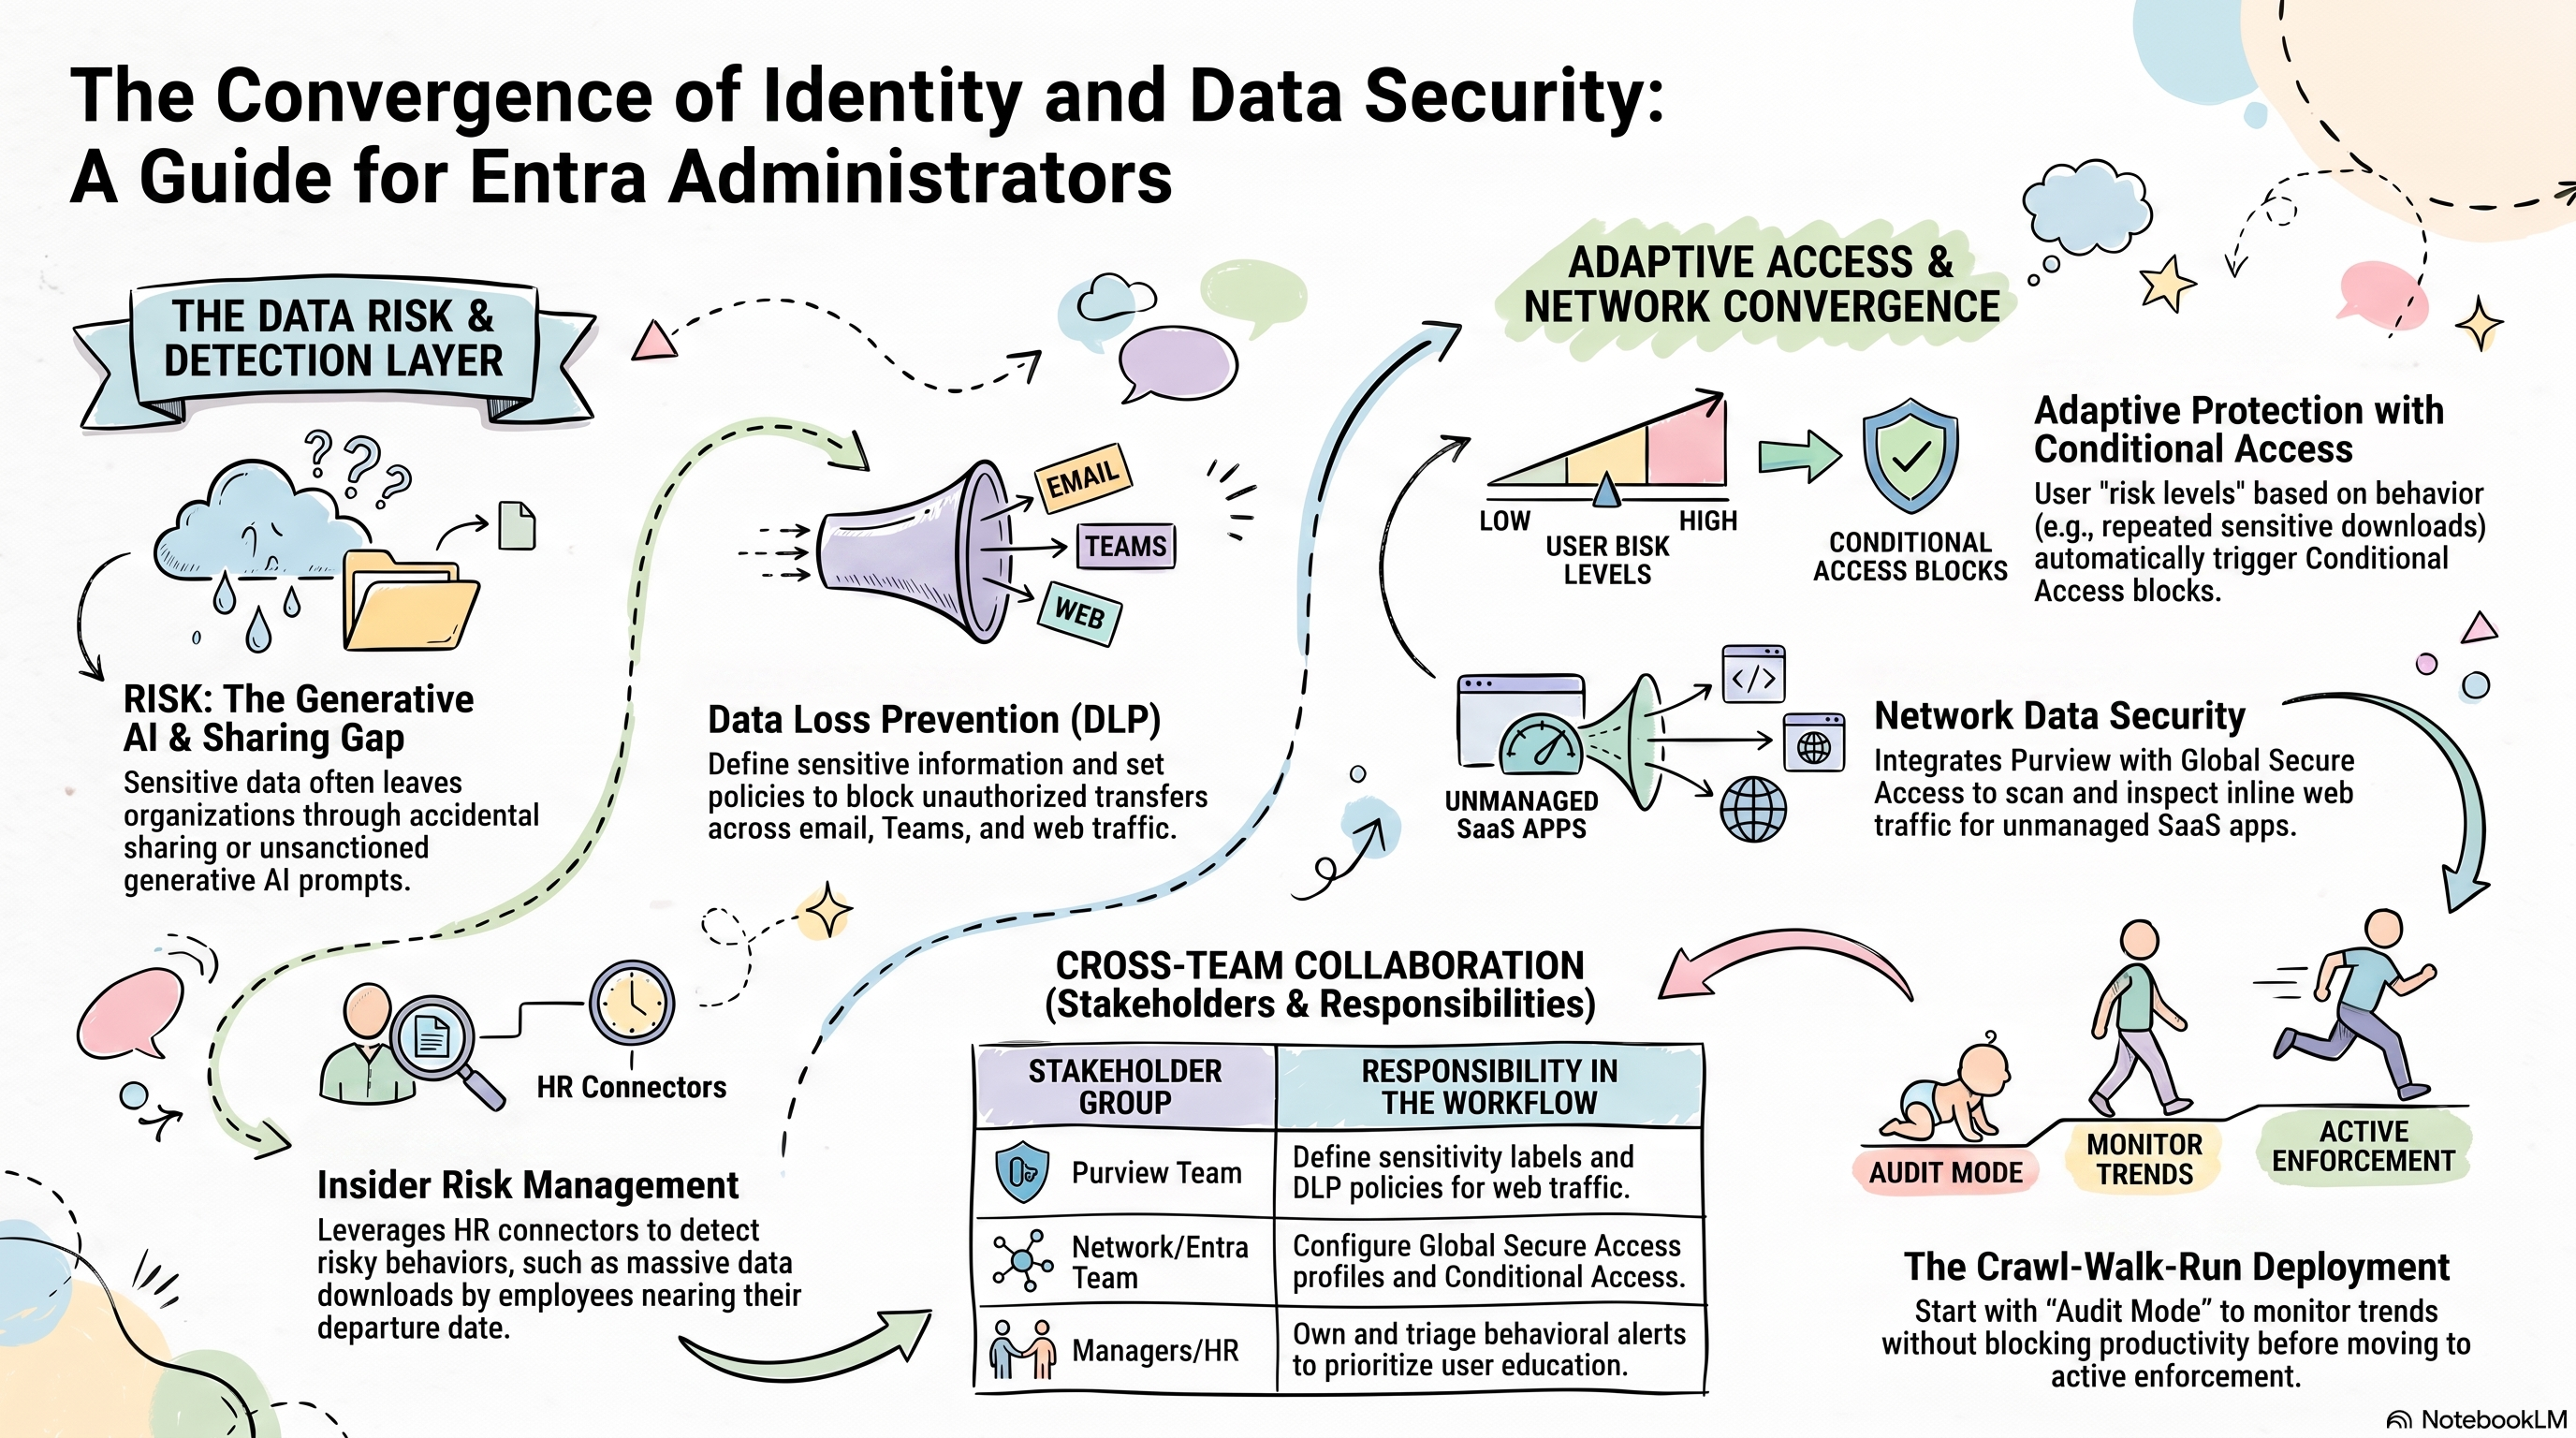 Why Entra Admins Need Microsoft Purview Now 28.07.2026 54mConditional Access no longer begins and ends with identity signals.Microsoft Purview can now influence the controls Entra administrators are asked to implement. From insider-risk conditions in Conditional Access to inline protection for sensitive data moving toward unsanctioned AI apps. That means Entra teams need enough Purview knowledge to understand what triggers a policy, how users experience it, and who should respond when an alert fires.In this episode of Entra.Chat, Merill speaks with Ray Reyes, Principal Security Consultant at Engage Squared and author of Mastering Microsoft Purview De...
-
 How Xbox Secures 70+ Entra Tenants Every Night with Maester 20.07.2026 46mXbox Security runs a gaming-specific Microsoft Entra baseline across more than 70 tenants every night.The scale is striking: about 50 controls, dozens of independently operated game-studio tenants, and one parallel pipeline that checks whether each environment still matches Xbox’s security intent. When a Conditional Access policy moves to report-only or a required service principal loses a permission, the next run finds it.In this episode of Entra.Chat, Merill speaks with Audrey Long, Principal Cloud Security Architect in Xbox Security at Microsoft, and Sam Erde, SecureShield Architect at Patr...
-
 One Compromised Agent ID Blueprint Can Cross Tenant Boundaries 12.07.2026 54mMicrosoft Entra Agent ID uses familiar application and service-principal objects under the hood, but its one-to-many hierarchy creates a different security boundary. A blueprint can be associated with many agent identities. When that blueprint belongs to a third-party provider and is trusted across customer tenants, the provider’s credential security becomes part of every customer’s risk model.In this episode of Entra.Chat, Merill speaks with Katie Knowles, Senior Security Researcher at Datadog, about her three-part security analysis of Microsoft Entra Agent ID. Katie explains the blueprint, b...
-
 Attackers Are Targeting The AI Ecosystem You Cannot See 04.07.2026 44mAI agent security is not just about attackers using AI.It is also about attackers targeting the agent ecosystem most organizations cannot see clearly yet: MCP servers, agent skills, packages, API keys, prompts, tools, and the identity layer underneath all of it.In this episode, I sit down with Thomas Roccia, founder of Security Break and a former Microsoft threat researcher, to look at AI agents from the threat-intelligence side. Thomas explains why the easiest path for attackers may not be futuristic autonomous hacking. It may be the boring weak spots that already exist: malicious packages, u...
-
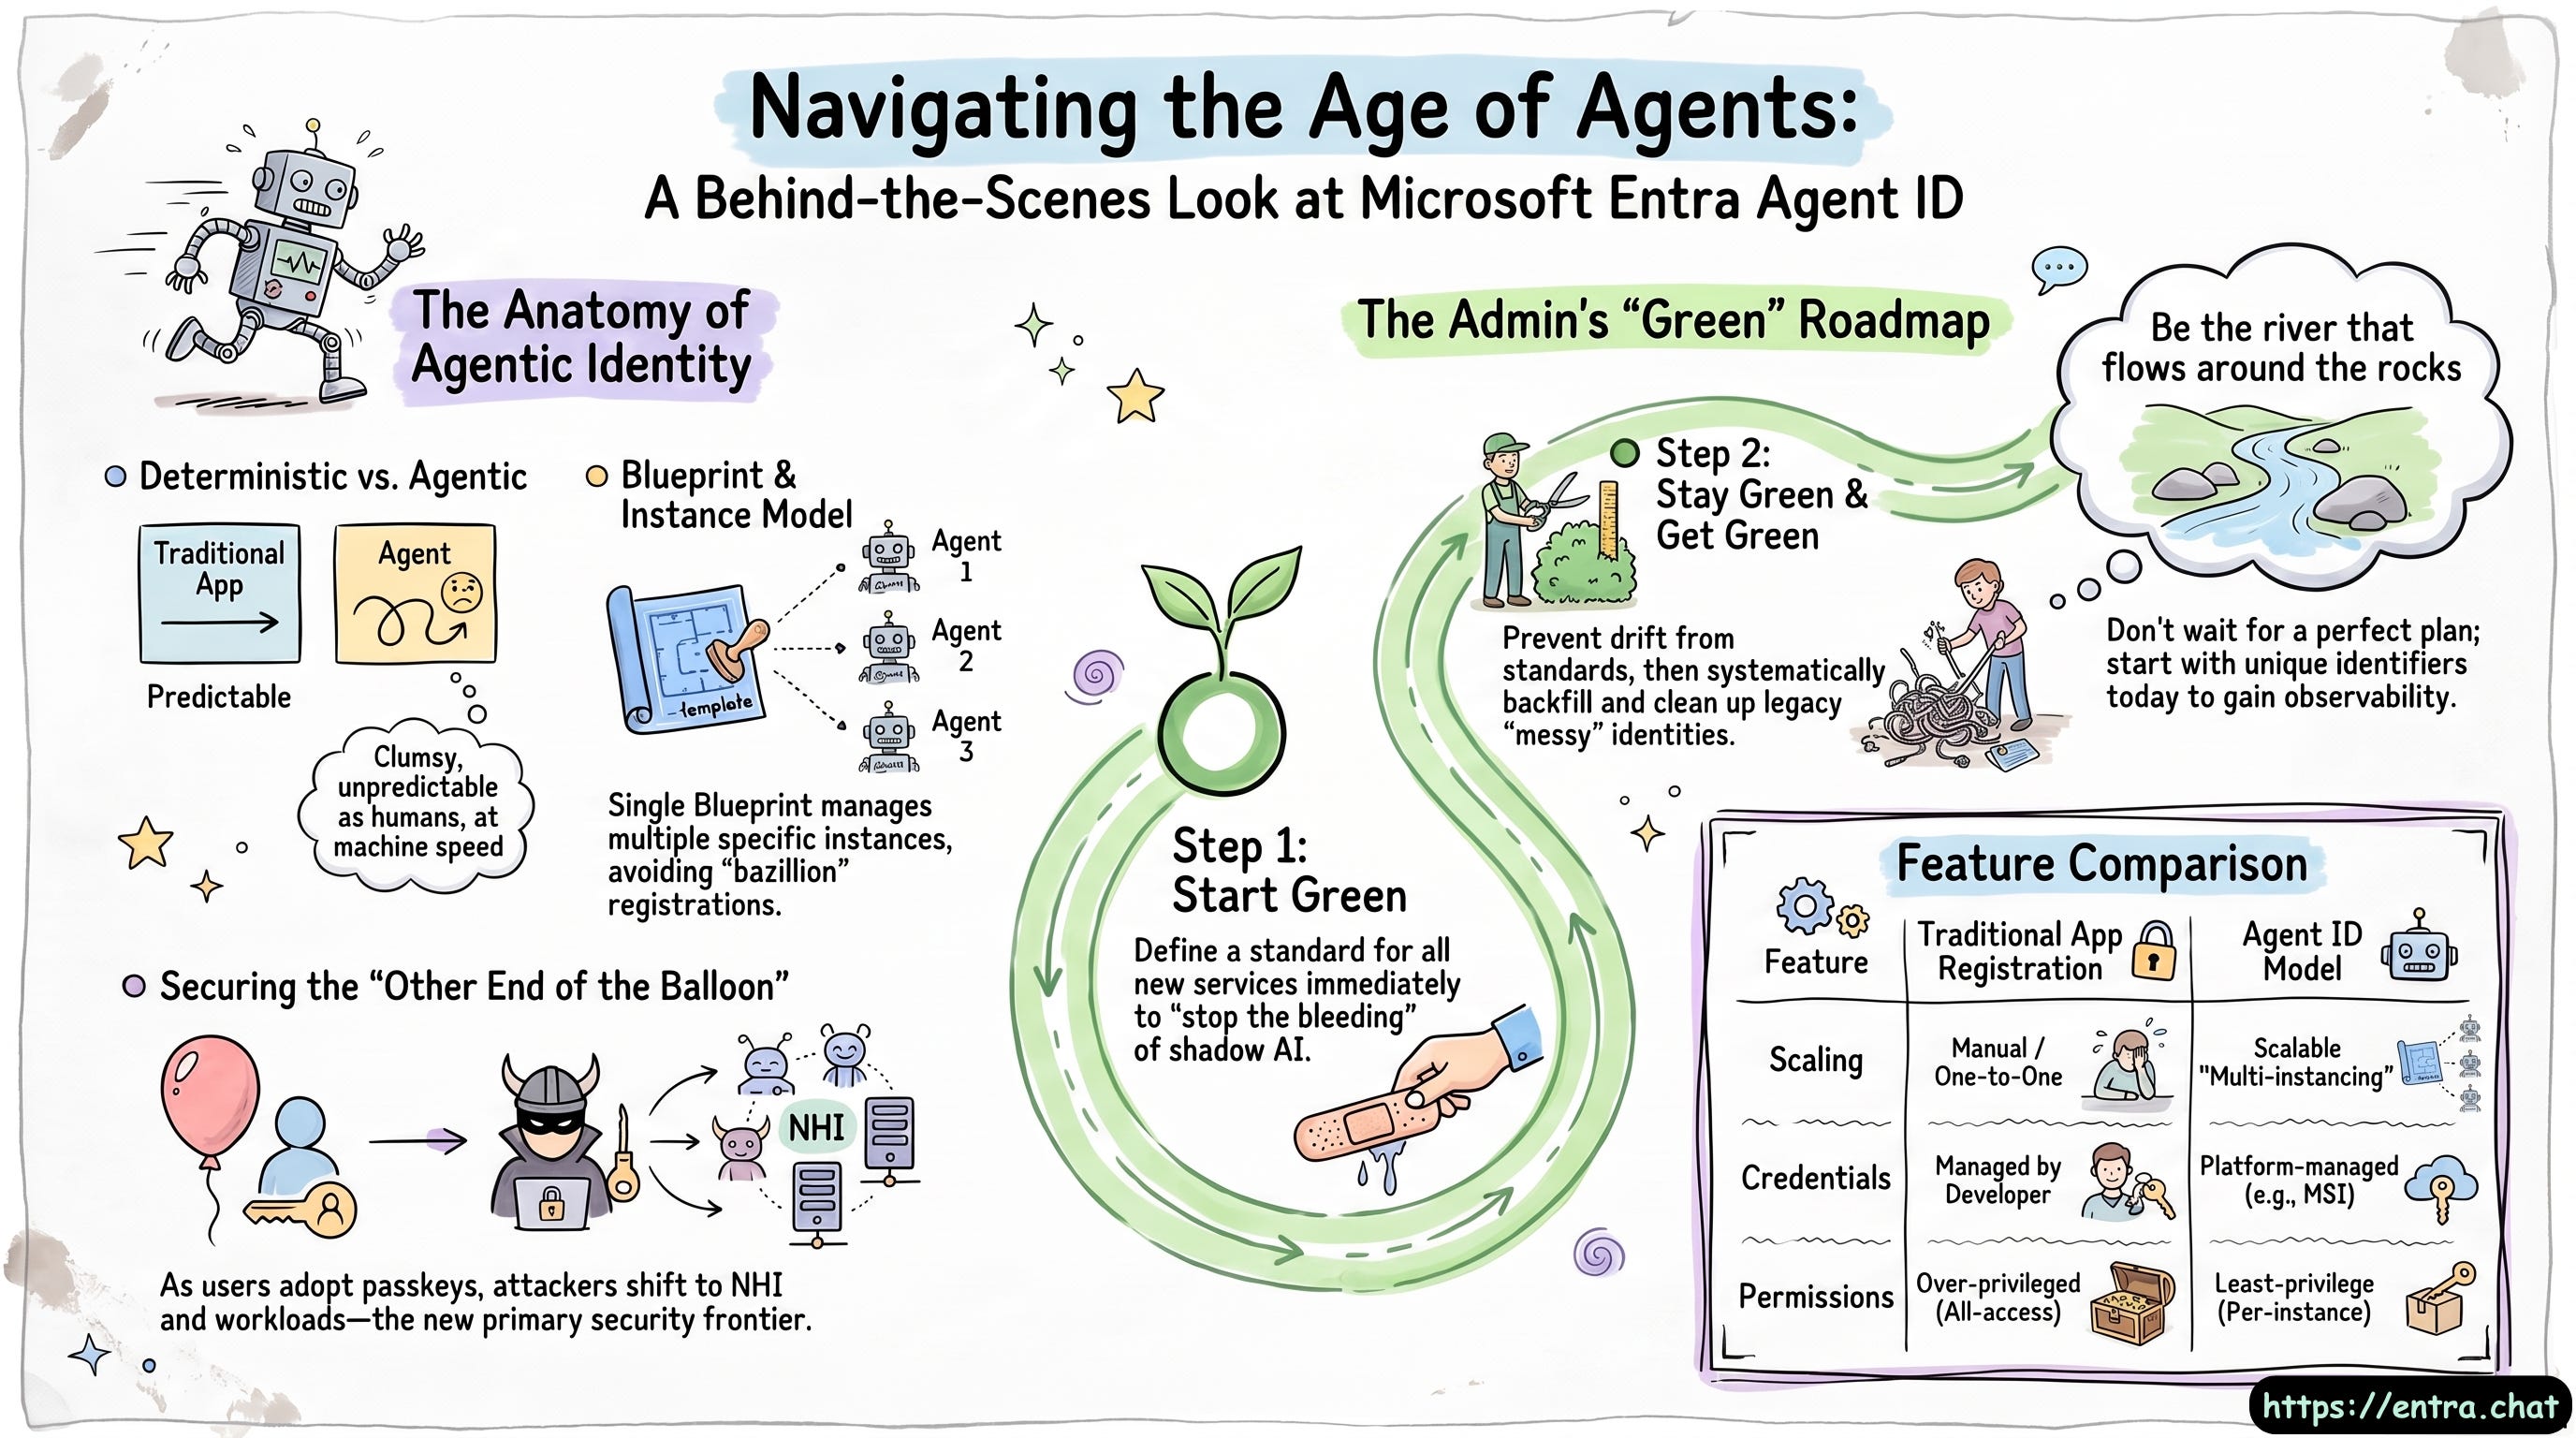 From Windows Core to Leading Agent ID: Vince Smith’s Microsoft Story 28.06.2026 47mFolks, every big thing in identity started as somebody’s late-night side quest and Vince Smith has been in the room for a lot of them. In this episode of Entra Chat, Vince (the PM lead driving Microsoft Entra Agent ID) walks us back through a 25-year run at Microsoft: shipping beta products off a machine wired straight to the internet under a neighbor’s desk, owning the early RBAC and custom roles work that shaped Entra, surviving a couple of security incidents he mostly can’t talk about, and finally landing on the team building identity for AI agents. Along the way he owns up to the one featu...
-
 Shadow Admins: The Non-Human Identities Hiding in Your Entra Tenant 20.06.2026 1h 8mNot every admin in your tenant is a person. Service principals, app registrations, and the new wave of agent identities can quietly hold permissions powerful enough to own your entire environment and most orgs can’t even see them. In this episode of Entra Chat, we sits down again with Erika Zellig to expose the “shadow admins” hiding in your Entra tenant, and what to do about them.What we get into:* Application vs. delegated API permissions and why both can be shadow admins* The most dangerous permissions to hunt for: Files.ReadWrite.All, Sites.FullControl.All and more.* How Midnight Blizzard...
Similar podcasts


Popular in
The podcast also appears in the podcast charts of these countries.
