
The InfoSec Control Room
The InfoSec Control Room is a cybersecurity podcast hosted by Taher Amine ELHOUARI, focusing on governance, risk, compliance, resilience, and CISO-level decision-making. It explores the gap between what organizations believe they have in place and what actually works during incidents, audits, regulatory questions, and risk-based decisions. Topics include information security, GRC, CISO leadership, ISO standards, cyber resilience, privacy, incident response, CSIRT operations, security awareness, and regulatory expectations. The core premise is that most organizations have a governance problem that manifests as security. The show targets CISOs, security leaders, GRC professionals, auditors, consultants, and practitioners.
Episodes
-
 EP020: The Most Dangerous Risk Is the One Everyone Already Knows About 15.11.2026 7mTaher Amine ELHOUARI explores why long-standing cyber risks can become more dangerous as organizations grow accustomed to them, examining legacy systems, recurring exceptions, unclear ownership, delayed treatment, and the difference between knowing about a risk and actually doing something about it.
-
 EP019: Third-Party Assurance Is More Than a Questionnaire 13.11.2026 8mTaher Amine ELHOUARI explores why supplier assurance requires more than questionnaires, examining evidence, certifications, access, dependency, incidents, contractual expectations, changing supplier relationships, and how organizations can decide how much trust a third party has actually earned.
-
 EP018: Who Actually Owns the Data? 26.10.2026 9mTaher Amine ELHOUARI explores what data ownership actually means, examining access, classification, sharing, retention, deletion, third parties, AI tools, and why real ownership requires business authority rather than simply assigning a name in a governance matrix.
-
 EP017: The Cybersecurity KPI Problem 25.10.2026 11mTaher Amine ELHOUARI explores why cybersecurity KPIs can mislead when they measure activity instead of outcomes, and how organizations can choose metrics that improve decisions rather than simply improve dashboards.
-
 EP016: Your SOC Is Busy. But Is It Effective? 20.10.2026 14mTaher Amine ELHOUARI examines why a busy SOC is not necessarily an effective SOC, exploring alert fatigue, false positives, detection coverage, analyst workload, visibility gaps, escalation, automation, and the difference between security activity and meaningful outcomes.
-
 EP015: The Future CISO Is a Trust Leader, Not a Security Manager 19.10.2026 17mTaher Amine ELHOUARI explores how the CISO role is evolving beyond traditional security management toward business trust, examining customer confidence, product security, AI, resilience, communication, commercial enablement, reputation, and the leadership skills required of the modern CISO.
-
 EP014: The Risk Register Is Not Risk Management 10.10.2026 20mTaher Amine ELHOUARI explores why maintaining a cyber risk register is not the same as managing risk, covering risk ownership, treatment delays, scoring, acceptance, changing evidence, business trade-offs, prioritization, and the decisions that make risk management real.
-
 EP013: You Outsourced the Service, Not the Risk 12.09.2026 17mTaher Amine ELHOUARI explores why outsourcing a service does not outsource the associated risk, covering supplier dependency, shared responsibility, third-party access, contracts, incident handling, concentration risk, offboarding, and the internal capability needed to govern providers effectively.
-
 EP012: Cyber Resilience — What Happens After Prevention Fails 07.09.2026 17mTaher Amine ELHOUARI explores cyber resilience beyond prevention, examining how organizations can keep critical services functioning, manage dependencies, recover effectively, adapt during disruption, and improve after failures and incidents.
-
 EP011: ISO 27001 Is Not the Certificate on the Wall 05.09.2026 15mTaher Amine ELHOUARI explores why ISO/IEC 27001 certification should be the result of a functioning ISMS rather than the end goal, and examines risk ownership, internal audit, corrective action, management review, control implementation, and continuous improvement beyond audit day.
-
 EP010: The Board Does Not Need Another Cyber Dashboard 04.09.2026 17mTaher Amine ELHOUARI explores why cybersecurity dashboards often overwhelm boards with activity instead of helping them make decisions, and explains how executive reporting should connect cyber risk, uncertainty, business impact, priorities, and required leadership action.
-
 EP009: Your CSIRT Is Not Ready Just Because It Exists 03.09.2026 25mIn EP009 of The InfoSec Control Room, I look beyond the simple statement, “We have a CSIRT,” and ask the question that actually matters: what can that team really do when something serious happens?A CSIRT can exist on the organization chart, have assigned staff, procedures, tooling, and even a dedicated mailbox, while still being poorly prepared for a real incident. Readiness comes from much more practical things: knowing exactly what the team is responsible for, who it serves, how people reach it, what happens outside business hours, what access responders already have, how cases are handed o...
-
 EP008: Stop Lying to Yourself About Cyber Maturity 22.08.2026 26mTaher Amine ELHOUARI examines why cybersecurity maturity scores can create false confidence and explains how organizations should measure real capability through evidence, operating effectiveness, risk context, testing, metrics, and independent challenge.
-
 EP007: Incident Response Starts Before the Incident 16.08.2026 28mTaher Amine ELHOUARI explains why incident response begins long before the first alert fires, exploring authority, escalation, communications, SOC and CSIRT coordination, backups, business continuity, executive decision-making, exercises, and the organizational preparation required for real cyber resilience.
-
 EP006: Your Policy Is Not a Control 15.08.2026 24mTaher Amine ELHOUARI explores why having an approved security policy does not automatically mean an organization has control, and how policies must be translated into real behavior, ownership, technical enforcement, evidence, monitoring, and accountability.
-
 EP005: GRC and SecOps Are Speaking Different Languages 14.08.2026 25mTaher Amine ELHOUARI explores why GRC and SecOps must stop operating as separate worlds, and how connecting governance context with SOC and CSIRT operational evidence can improve control effectiveness, risk management, audit assurance, incident response, and executive decision-making.
-
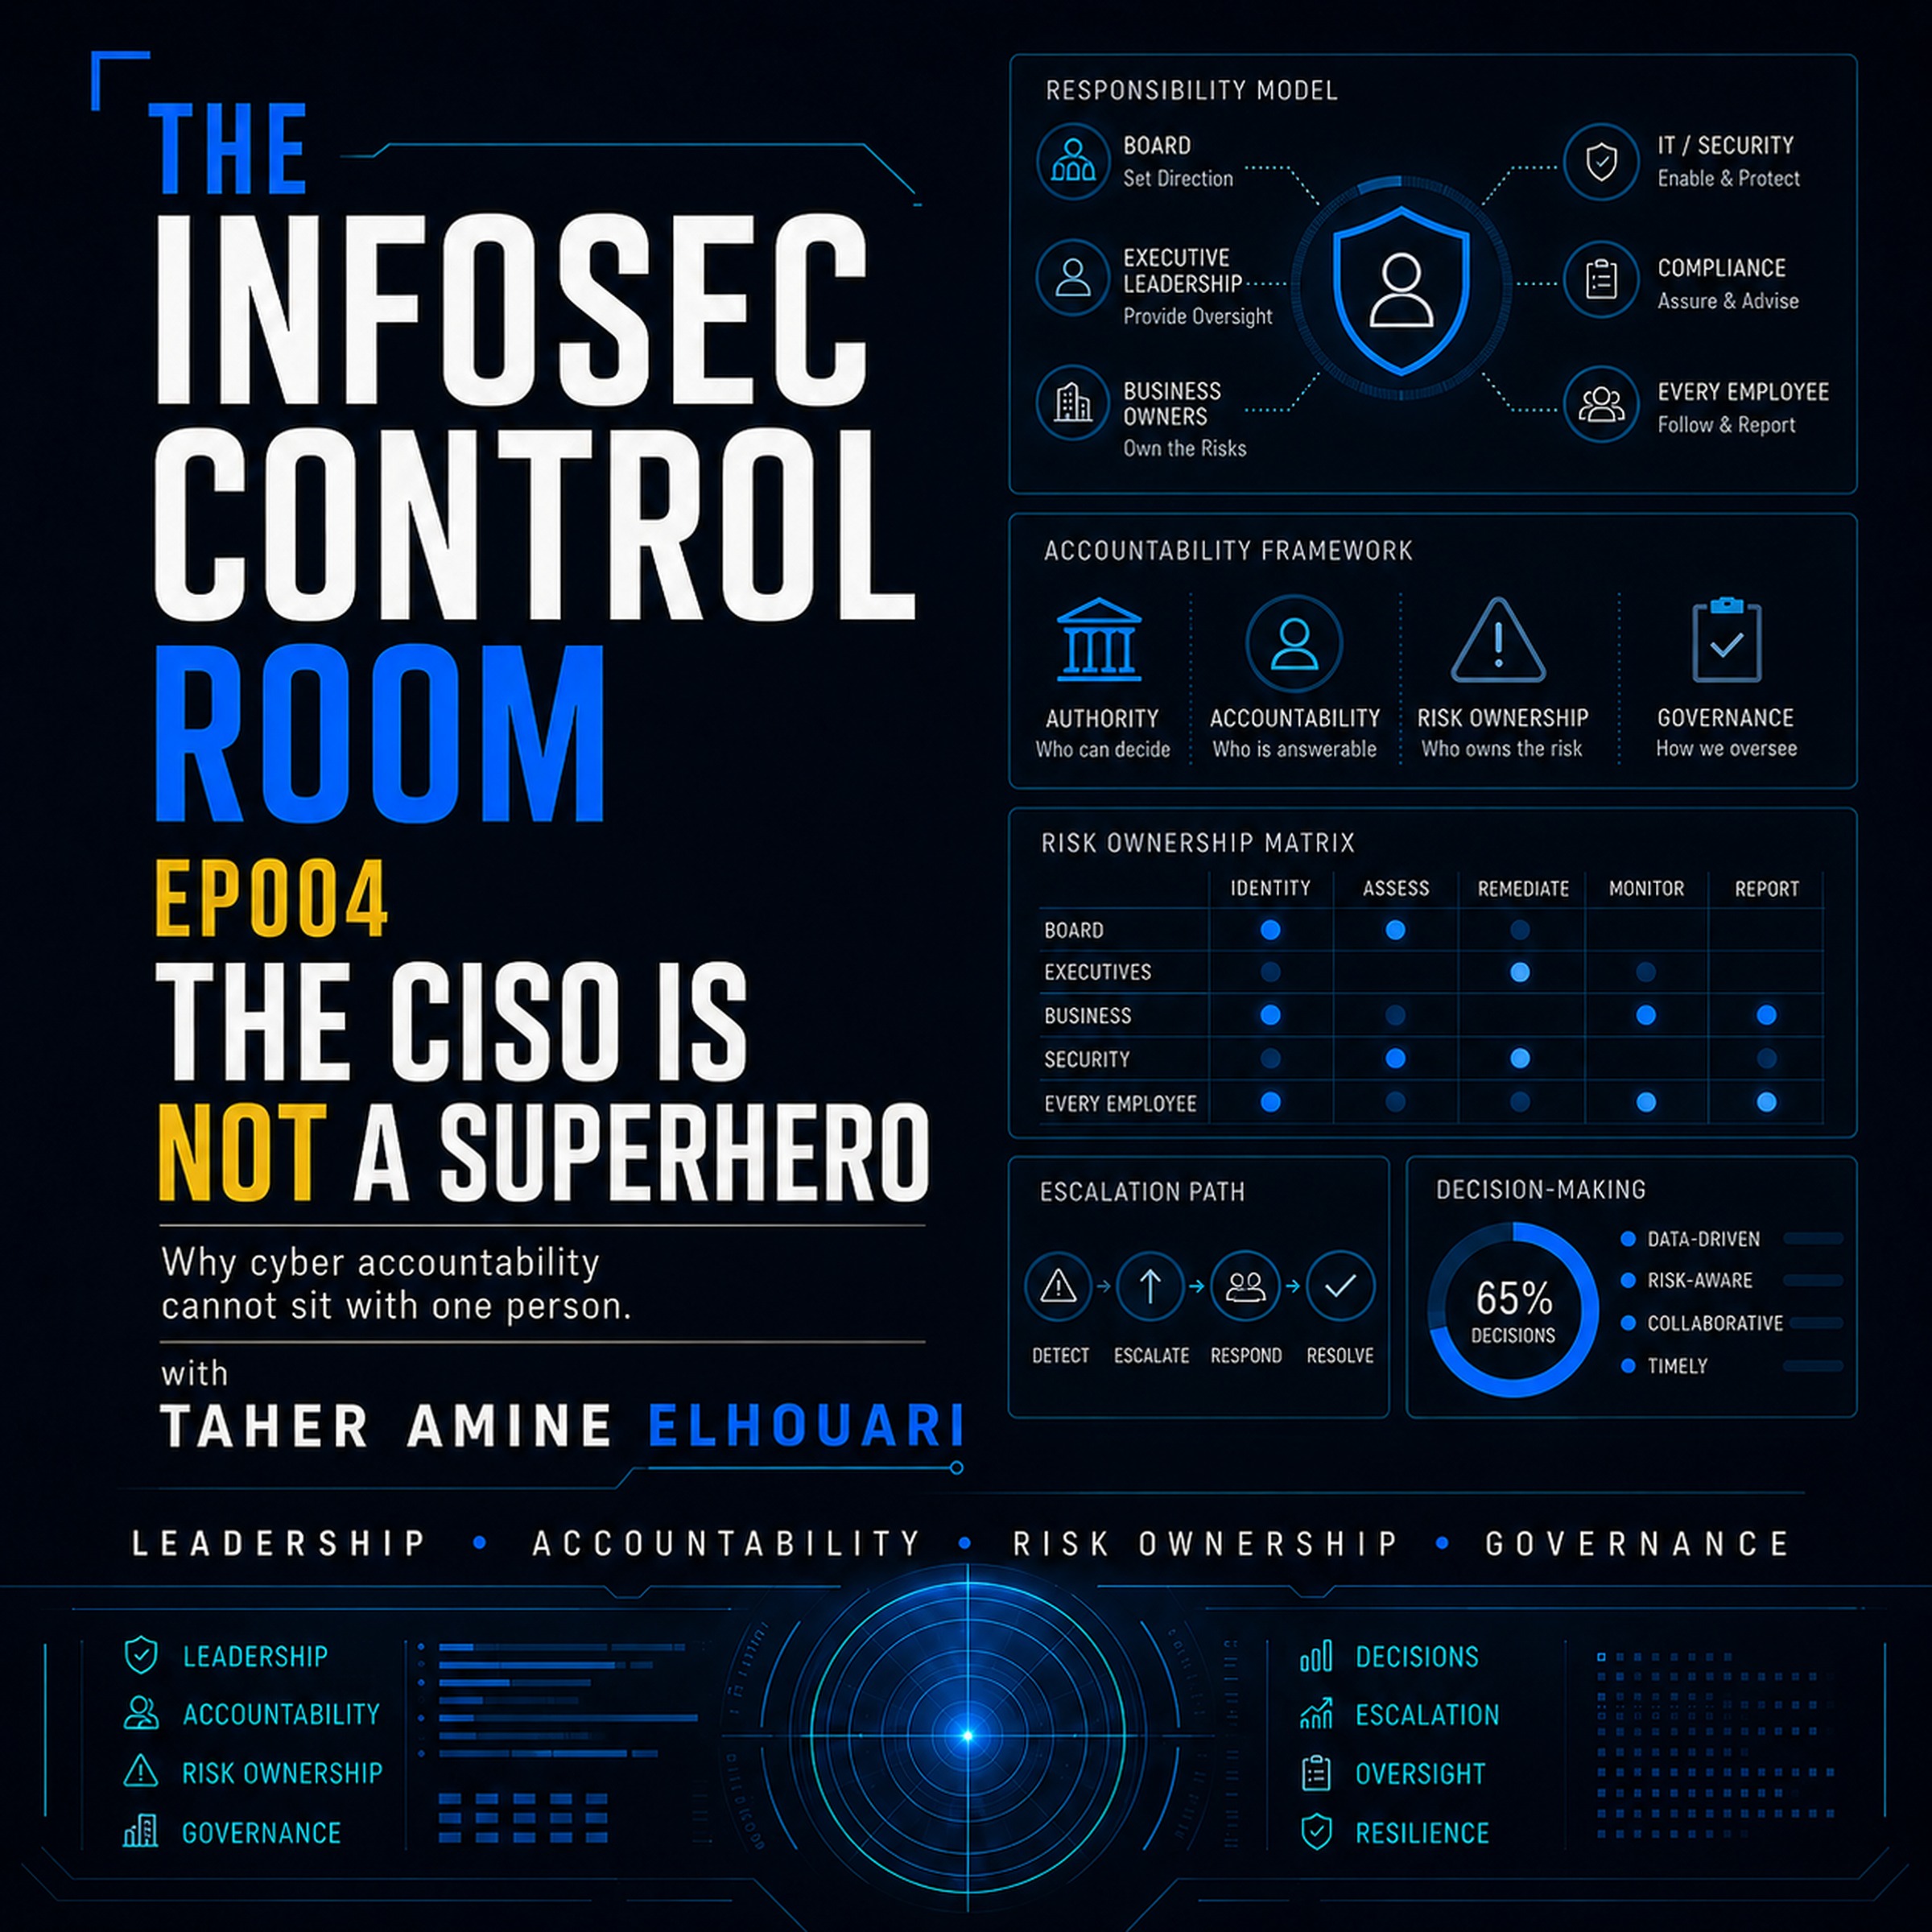 EP004: The CISO Is Not a Superhero 13.08.2026 24mCybersecurity cannot be owned by one job title. Taher Amine ELHOUARI explores what a CISO should actually be responsible for, why business and risk ownership must remain distributed across the organization, and how the CISO can act as a governance architect connecting security, operations, management, and executive decision-making.
-
 EP003: Compliance Is Not Control 12.08.2026 33mCompliance is not the same as control. Taher Amine ELHOUARI explores why passing audits, maintaining policies, and achieving certification do not automatically prove security effectiveness; and how organizations can move from checkbox compliance to real control, evidence, assurance, and resilience.
-
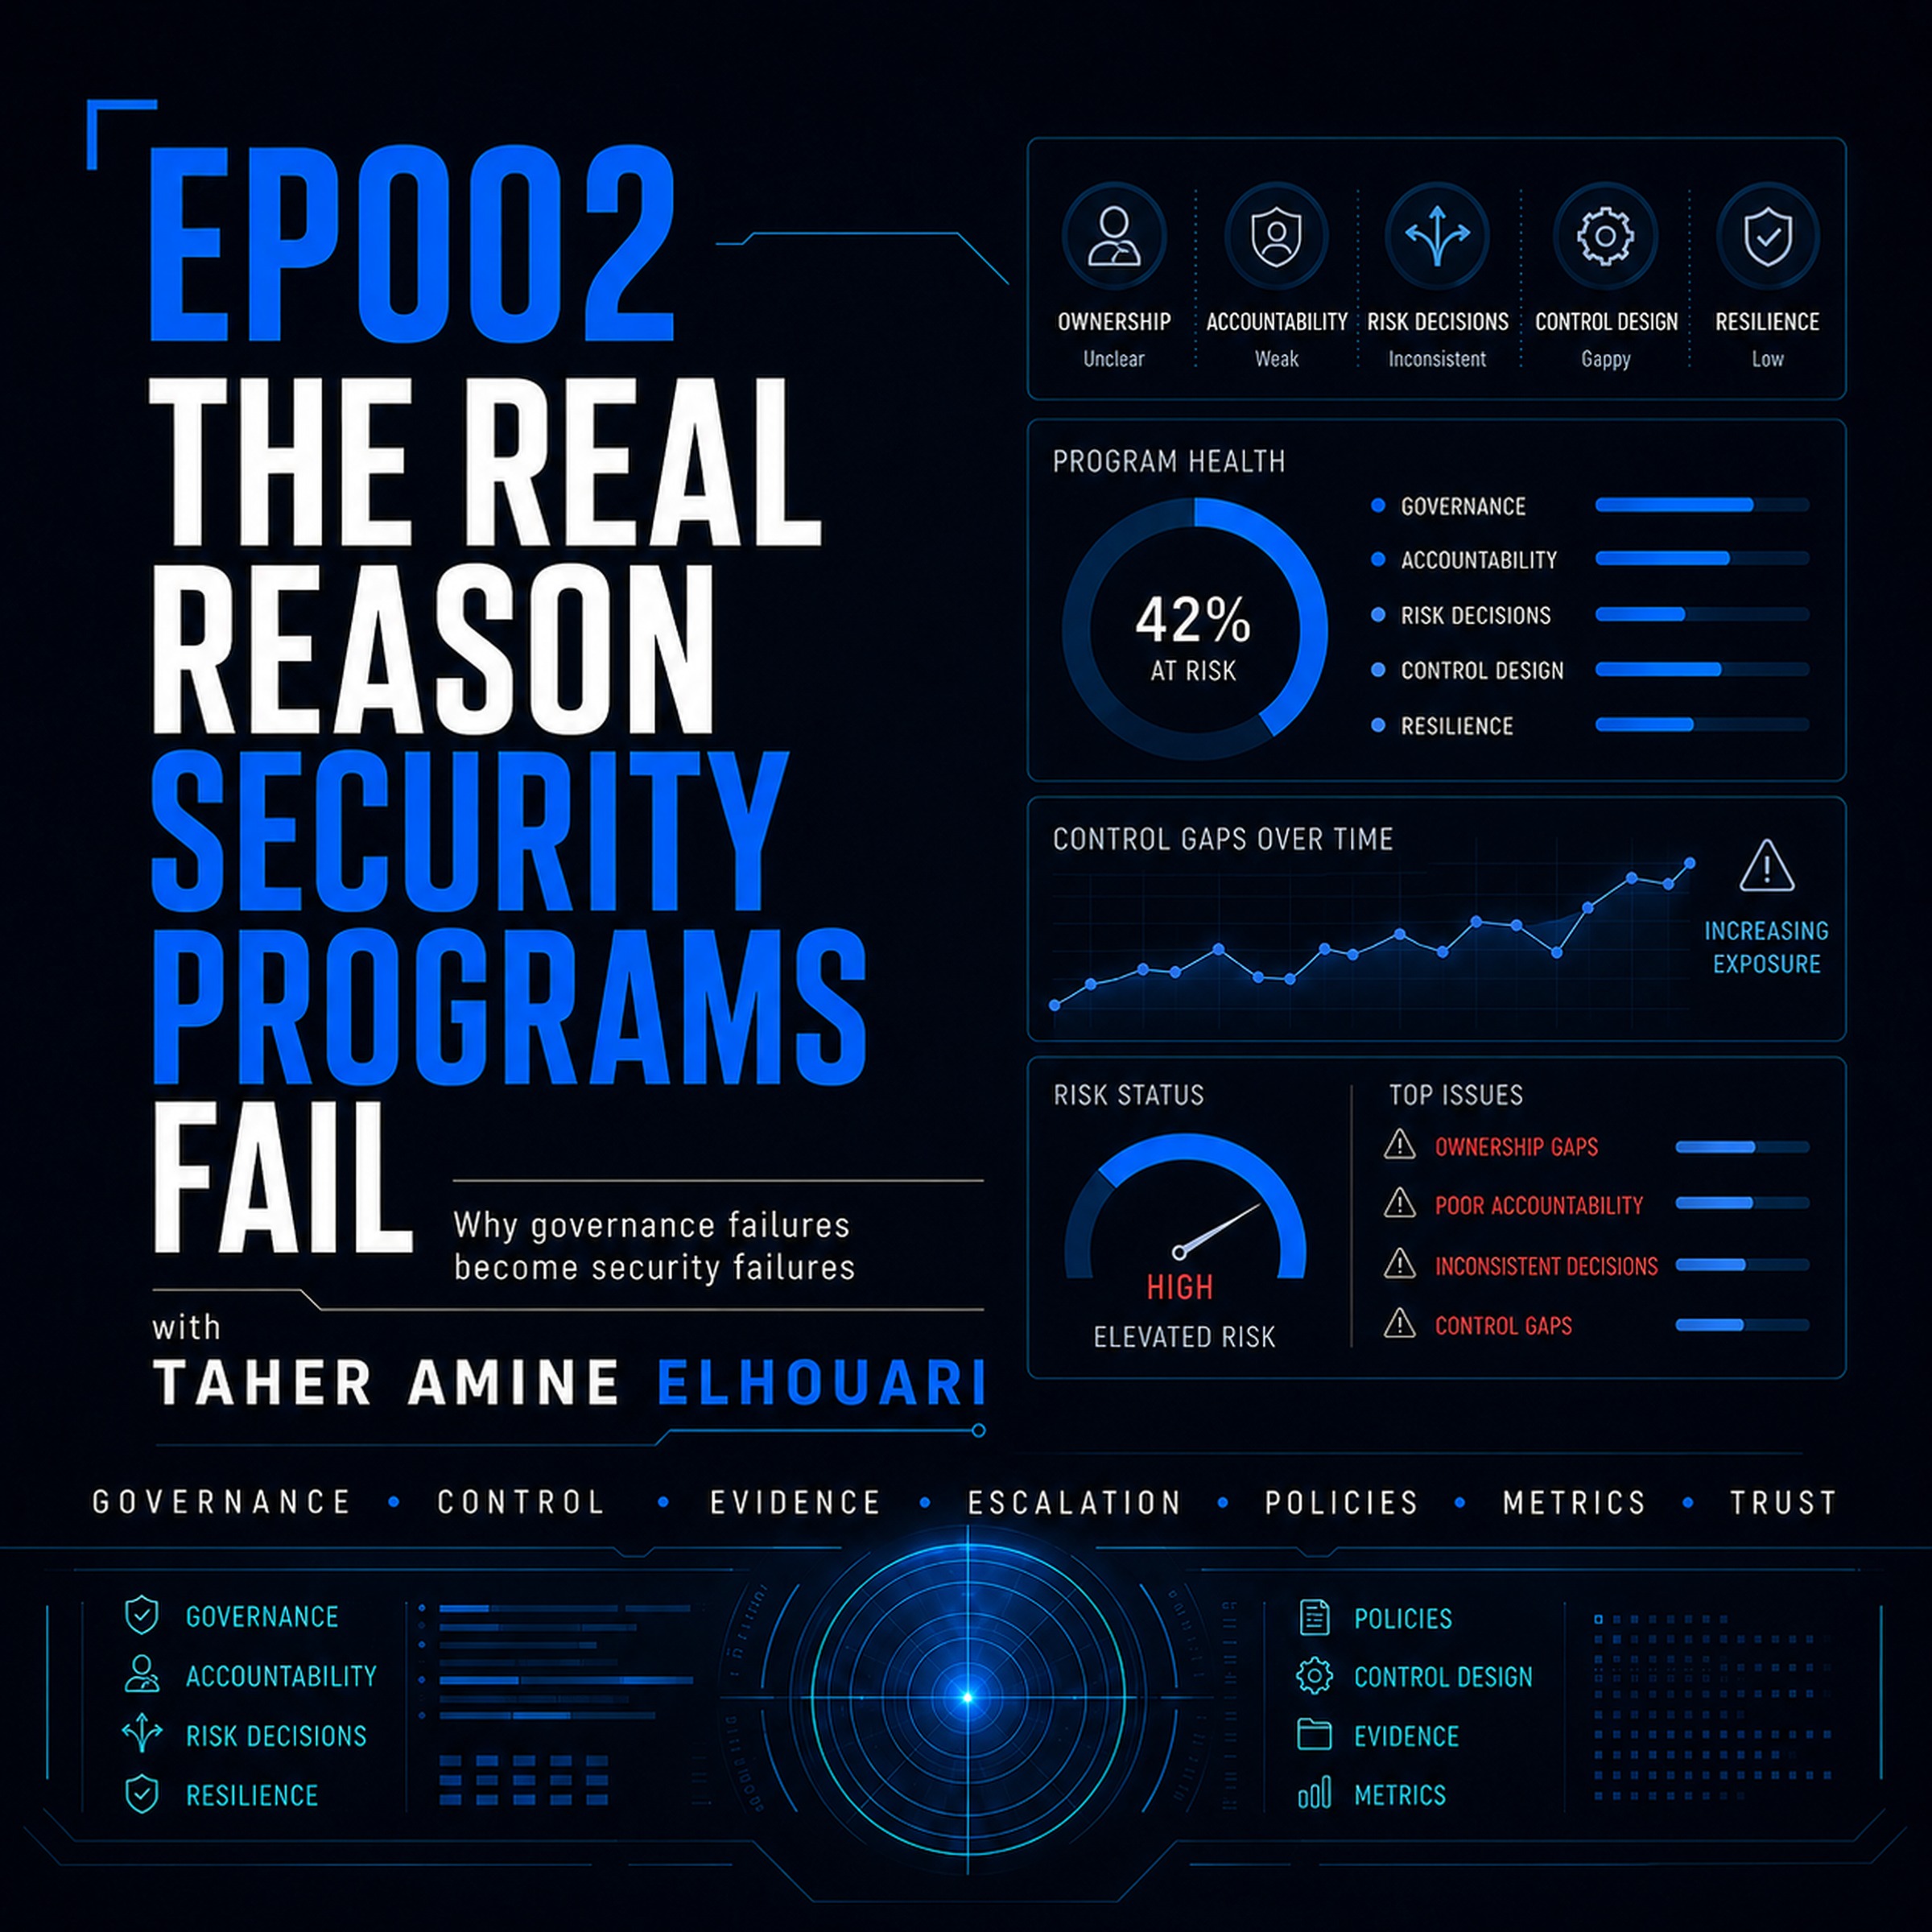 EP002: The Real Reason Security Programs Fail 12.08.2026 30mTaher Amine ELHOUARI explains why many security programs fail for reasons that are not purely technical, exploring governance gaps, weak ownership, poor risk decisions, ineffective controls, compliance theater, and the difference between security activity and real security capability.
-
 EP001: Welcome to The InfoSec Control Room 10.08.2026 31mThe official opening episode of The InfoSec Control Room, where Taher Amine ELHOUARI introduces the podcast, his background, the governance-first philosophy behind the show, and the mission of helping professionals understand how cybersecurity is governed, controlled, measured, and improved.
Similar podcasts


Popular in
The podcast also appears in the podcast charts of these countries.
